
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

D
Docker
V
V2EX
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
云风的 BLOG
云风的 BLOG
Blog — PlanetScale
Blog — PlanetScale
Recent Announcements
Last Week in AI
Last Week in AI
博客园 - Franky
Microsoft Security Blog
Hugging Face - Blog
Hugging Face - Blog
H
Hackread – Cybersecurity News, Data Breaches, AI and More
Vercel News
Vercel News
MyScale Blog
MyScale Blog
大猫的无限游戏
大猫的无限游戏
罗磊的独立博客
H
Help Net Security
月光博客
月光博客
Martin Fowler
Martin Fowler
博客园 - 【当耐特】
宝玉的分享
宝玉的分享
P
Proofpoint News Feed
GbyAI
GbyAI
腾讯CDC
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More

www.infosecurity-magazine.com

Just Three Ransomware Gangs Accounted for 40% of Attacks Last Month Google Chrome Rolls Out Protection Against Infostealers Targeting Session Cookies STX RAT Targets Finance Sector With Advanced Stealth Tactics Bitcoin Depot Reports $3.6m Crypto Theft After System Breach Atomic Stealer MacOS ClickFix Attack Bypasses Apple Security Warnings Middle East Hack-for-Hire Operation Traced to South Asian Cyber Espionage Group Governance Gaps Emerge as AI Agents Drive 76% Increase in NHIs Google Warns of New Threat Group Targeting BPOs and Helpdesks Google API Keys Quietly Gain Access to Gemini on Android Devices Critical Vulnerability in Ninja Forms Exposes WordPress Sites Anthropic Launches Project Glasswing to Use AI to Find and Fix Critical Software Vulnerabilities US Thwarts DNS Hijacking Network Controlled by Russian APT28 Hackers Claude Discovers Apache ActiveMQ Bug Hidden for 13 Years Iran‑Backed Threat Actors Hit US CNI Providers via Internet‑Facing OT Assets Russian APT28 Hackers Hijack Routers to Steal Credentials, UK Security Agency Warns GPU Rowhammer Attack Enables Privilege Escalation and Full System Compromise GrafanaGhost Exploit Bypasses AI Guardrails for Silent Data Exfiltration Over $17bn Lost to Cyber Fraud in the Last Year, Warns FBI Storm-1175 Exploits Flaws in High-Velocity Medusa Attacks Fortinet Releases Emergency Patch After FortiClient EMS Bug Is Exploited New Phishing Platform Used in Credential Theft Campaigns Against C-Suite Execs New 'Storm' Infostealer Remotely Decrypts Stolen Credentials NCSC Issues Security Alert Over Hackers Targeting WhatsApp and Signal Accounts Apple Expands iOS 18 Security Updates Amid DarkSword Threat Researchers Observe Sub-One-Hour Ransomware Attacks GitHub Used as Covert Channel in Multi-Stage Malware Campaign Most CNI Firms Face Up to £5m in Downtime from OT Attacks Google Introduces Android Dev Verification Amid Openness Debate New Venom Stealer MaaS Platform Automates Continuous Data Theft Chinese Hackers Target European Governments in Espionage Campaigns
Everest Forms Pro Vulnerability Allows Remote Code Execut...
Alessandro Mascellino · 2026-06-05 · via www.infosecurity-magazine.com

A critical vulnerability in the Everest Forms Pro plugin for WordPress has been actively exploited to hijack vulnerable websites.

According to new analysis from WordPress security firm Wordfence, the remote code execution flaw lets unauthenticated attackers run PHP on a target server and take over the site.

Tracked as CVE-2026-3300, the bug scores 9.8 on the CVSS scale and affects every release up to and including 1.9.12. Everest Forms Pro is a commercial form builder from developer WPEverest, with roughly 4000 active installations.

The flaw was reported to Wordfence's bug bounty program by a researcher using the handle h0xilo.

WPEverest patched the flaw in version 1.9.13. Any site on an earlier build remains exposed, and administrators have been urged to update without delay.

Read more on WordPress plugin attacks: Major WordPress Plugin Flaw Exploited in Under 4 Hours

Single Quotes Slip Past Sanitization

At the core of the bug is the WordPress plugin's Calculation add-on, which runs a form's calculation formula through PHP's eval() function.

Submitted field values are concatenated into that PHP string before it runs, and sanitize_text_field() does not escape single quotes. An attacker can open a value with a quote, break out of the wrapping string and inject PHP that eval() then executes.

Only forms that switch on the "Complex Calculation" feature are exposed to the PHP code injection. On those, any text, email, URL, select or radio field can serve as the entry point.

From there, a successful attack can create rogue administrator accounts, plant webshells and open further footholds.

Rogue Admin Accounts and Blocked Attacks

Wordfence telemetry shows the attacks began on April 13, 2026, about two weeks after public disclosure. Its leading payload tried to register an administrator account named "diksimarina."

In total, the firm said its firewall has blocked more than 29,300 exploit attempts. A surge on May 16 accounted for over 17,900 of them in a single day.
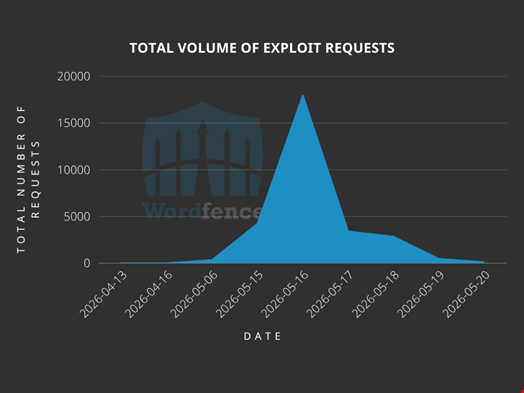
Credit: Wordfence.
Credit: Wordfence.

Defenders reviewing their logs should watch for the following indicators:

  • Administrator account using the name "diksimarina"

  • The email address diksimarina@gmail.com

  • Requests from 202.56.2.126, the source of more than 26,300 blocked attempts

Flaws that hand attackers administrator access have become a recurring problem for WordPress operators.