







Microsoft has cracked down on Fox Tempest, a cyber threat actor that fueled Rhysida ransomware attacks and developed tools for major malware strains like Oyster, Lumma Stealer, and Vidar.
On May 19, the tech giant unsealed a legal case in the US District Court for the Southern District of New York focused on the group.
It also shared details of how its Digital Crimes Unit (DCU) agents have engaged with Fox Tempest’s operators using undercover personas, identified the group’s infrastructure, collaborated with some of the organizations hosting this infrastructure and disrupted the group’s operations.
Microsoft is now working with the FBI and Europol’s European Cybercrime Centre (EC3) to uncover the identity of people behind the group.
Fox Tempest is a financially motivated threat actor that has been active since at least May 2025.
The group operates “in the upstream in the malware and ransomware supply chain, as an enabler,” Maurice Mason, principal cybercrime investigator at Microsoft's Digital Crimes Unit, explained during a press briefing held on May 18.
This means that, instead of carrying out malicious operations themselves, Fox Tempest provides tools and services enabling other cyber-threat actors to do so.
Specifically, the group sells what Microsoft calls a “malware-signing-as-a-service” (MSaaS) offering that further allows cybercriminals to disguise malware as legitimate software and thereby evade traditional security defenses.
Microsoft assessed that Fox Tempest has worked closely with several ransomware groups.
These include Storm-2501, Storm-0249 and Rhysida, a group tracked by Microsoft as Vanilla Tempest.
Rhysida, in particular, was named as a Fox Tempest’s co-conspirator in the lawsuit. The group has been linked to multiple cyber-attacks between 2023 and April 2026, including schools, hospitals, medical institutions and other critical infrastructure organizations worldwide.
Rhysida is also believed to be behind an October 2023 hack targeting the British Library and a data extortion attack against Seattle-Tacoma International Airport in September 2024.
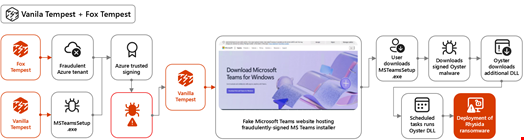
Additionally, the fraudulent code-signing tool developed by Fox Tempest was identified by Microsoft in the deployment of a number of malware strains including Aurora, Lumma Stealer, Malcert, Oyster, Vidar and many more.
It was also spotted in some campaigns deployed by MuddyWater, a cyber-espionage group attributed by several experts to Iran's Ministry of Intelligence and Security (MOIS).
Among the countries most targeted by Fox Tempest were the US, France and India, followed by China, Brazil, Germany, Japan, the UK, Italy and Spain.
“This doesn’t mean that these countries were targeted by malware or ransomware, but that there was a file on a machine in one of these countries that had been signed by a certificate made using the Fox Tempest-made code-signing service,” noted DCU’s Mason.
To build its MSaaS tool, Fox Tempest abused code-signing tools such as Microsoft’s Artifact Signing, a system introduced as Trusted Signing in 2024 and designed to help software developers verify that software is legitimate and hasn’t been tampered with.
“This fraudulent code-signing acts as a fake ID that lets cybercriminals get into the systems by walking right through the front door,” Steven Masada, global head of Microsoft DCU, explained.
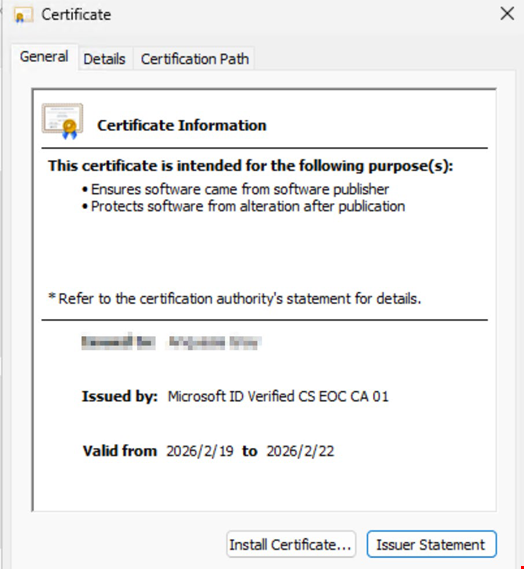
“It’s so scalable and easy for anyone to use, even for the most non-technical person. You just need to drag and drop a file into a portal and it gets your software signed with Afrtifact Signing.”
After engaging with SamCodeSign, a seller of code-signing certificates since at least 2020 who acted as an access broker for Fox Tempest, the DCU team observed that they typically sell their service under three options:
Microsoft also collaborated with cybersecurity company Resecurity to explore how Fox Tempest operates.
The DCU then investigated Fox Tempest’s infrastructure, which initially included a website called Signspace[dot]cloud, using legitimate hosting providers like UK-based Freak Hosting, and Estonia-based Wavecom as the service’s virtual private server (VPS) suppliers.
The DCU team shifted its infrastructure in January 2026 and started using Cloudzy, another legitimate VPS provider based in Dubai, in the United Arab Emirates.
On May 5, Microsoft filed a civil court action with the Court for the Southern District of New York and was granted a court order three days later.
The DCU transferred the groups’ malicious domains to a Microsoft-owned sinkhole, disabled hundreds of virtual machines hosted on Cloudzy with the help of the provider, took down approximately 1000 accounts, and suspended the threat actor’s repository.
The DCU team then engaged with SamCodeSign, which shared the issues it was experiencing operating the service. “He’s freaking out, he’s upset, he won’t sell us a certificate anymore,” said DCU’s Mason.
Microsoft also observed a significant decrease in Fox Tempest-made certificates.
“Every day, we decide what software to trust in seconds guided by simple labels such as ‘verified,’ ‘secure’ and ‘safe to install.’ The problem is that those signs can be manipulated,” said Masada.
“For the first time, Microsoft is taking public action against a powerful, but often unseen, enabler within the cybercrime ecosystem, targeting how cybercriminals prepare and employ techniques to optimize their rate of success.”
Image credit: gguy / Shutterstock.com
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。