






A global surge in mobile banking malware targeting 1243 financial brands across 90 countries is reshaping the fraud landscape, with attacks now originating primarily on user devices, according to Zimperium zLabs.
Zimperium's latest report examined 34 active malware families affecting apps with more than three billion downloads, revealing what analysts describe as industrialised, large-scale campaigns.
These operations are reportedly evolving faster than traditional banking defences, driven by widespread code sharing and low barriers to entry for attackers.
Mobile banking is now the dominant channel for consumers, Zimperium said, with 54% relying on apps to manage accounts. As usage has increased, so has exposure to risk.
The report highlights a sharp rise in malicious activity, including a 56% increase in Android banking trojan attacks in 2025 and a 271% jump in unique malware packages to 255,090. Online fraud rose 21% between 2024 and 2025, while one in 20 verification attempts is now considered fraudulent. Overall, 80% of fraud occurs through online or mobile platforms.
"Mobile banking applications are absolutely a prime target," Boris Cipot, senior security engineer at Black Duck, commented. "As the research shows, more than 1200 financial apps are currently under active attack, and malware-driven fraud has increased 67% year over year."
Attackers are exploiting weak points in mobile applications. More than 60% of banking apps lack basic code protection, allowing criminals to reverse engineer systems and tailor attacks before targeting users.
Modern malware has progressed beyond credential theft, Zimperium warned, enabling attackers to control devices and operate within legitimate banking sessions. As a result, fraudulent activity often appears indistinguishable from normal user behaviour.
Read more on mobile banking fraud: GodFather Malware Upgraded to Hijack Legitimate Mobile Apps
"Today's malware families don't just steal credentials, they intercept authentication codes, monitor live sessions, and convincingly mimic legitimate app behavior," Cipot said. "In many cases, attackers are effectively taking control of the device itself."
Three malware families, TsarBot, CopyBara and Hook, accounted for more than 60% of banking and fintech app targeting. New variants such as Sturnus and Crocodilus introduce advanced techniques, such as "blackout" modes, that allow transactions to occur while a device appears inactive.
"The frontline of financial fraud has migrated from backend infrastructure to the customer's mobile device," Jason Soroko, senior fellow at Sectigo, said. "With threat actors deploying automated trojans to hijack legitimate banking sessions, traditional server-side fraud controls are rendered blind."
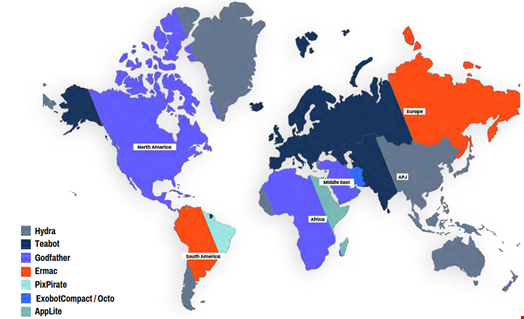
The threat is global but unevenly distributed, Zimperium warned. The US has 162 targeted banking apps, the highest concentration worldwide, followed by the UK with 69, Spain with 65 and Italy with 52. Rapidly digitizing markets, including India (42), Vietnam (23) and Malaysia (17) are also heavily targeted.
Artificial intelligence is accelerating attacks, enabling faster reverse engineering and the use of deepfakes to bypass identity checks.
The researchers concluded that financial institutions must prioritise mobile app security to defend against such threats, as backend-focused defences alone are no longer sufficient.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。