





An Iran-nexus cyber threat actor has been targeting government officials in Iraq by impersonating Iraq’s Ministry of Foreign Affairs, with the use of AI tools.
Government–related infrastructure in Iraq was compromised and used to host malicious payloads distributed as part of this campaign.
The campaign was detected in January 2026 by Zscaler ThreatLabz, which track the threat actor as Dust Specter and have attributed it to Iran “with medium to high confidence.”
ThreatLabz discovered the use of previously undocumented malware in this campaign, including Split Drop, TwinTask, TwinTalk and GhostForm.
The researchers also observed several fingerprints in the codebase indicating that Dust Specter leveraged generative AI for malware development.
The malicious campaign has been deployed following two distinct attack chains.
The first attack chain involves the delivery of a password-protected RAR archive named mofa-Network-code.rar. A 32-bit .NET binary, disguised as a WinRAR application, is present inside this archive and starts the attack chain on the endpoint. ThreatLabz called this binary SplitDrop.
This binary functions as a dropper for TwinTask and TwinTalk, two malicious dynamic-link library (DLL) files.
TwinTask’s main purpose is to poll a file for new commands available for execution and run them using PowerShell to ensure persistence on the target environment.
TwinTalk functions as a command-and-control (C2) orchestrator, the main purpose of which is to poll the C2 server for new commands, coordinate with the worker module and exfiltrate the results of command execution.
TwinTask and TwinTalk work in parallel to implement a file-based polling mechanism used for code execution.
In the report about this campaign, published on March 2, the ThreatLabz researchers said that the TwinTalk C2 domain, was also used by Dust Specter in July 2025 to host a web page disguised as a Cisco Webex meeting invitation.
The web page included a link to download the legitimate Cisco Webex software and prompted the victim to choose the “Webex for Government” option, luring the victim into following the instructions to retrieve the meeting ID.
These instructions are a typical social engineering method employed by threat actors to implement ClickFix-style attacks.
The second attack chain consolidates all the functionality of the first attack chain into a single binary.
It uses Google Forms as a social engineering lure and in-memory PowerShell script execution to execute the commands received from the C2 server, reducing the filesystem footprint.
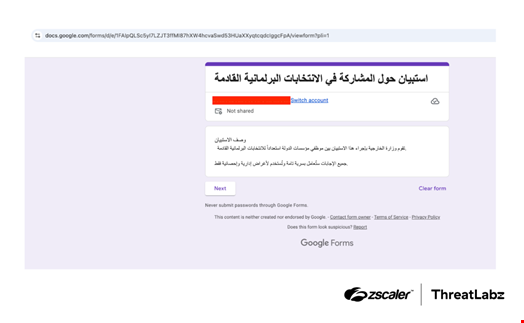
Unlike the first attack chain, the threat actor does not use a split architecture with DLL sideloading in this case. Instead, they use a .NET-based remote access trojan (RAT), dubbed GhostForm by ThreatLabz, that consolidates all the functionality of the first attack chain into one binary and uses in-memory PowerShell script execution.
ThreatLabz identified the use of emojis and unicode text in the codebase when decompiling TwinTalk and GhostForm.
“This unusual coding style strongly suggests that generative AI tools were utilized during the malware's development, and is a trend documented in other campaigns,” they wrote.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。