






A new Chinese-speaking cybercrime group has expanded its reach from East Asia into Europe and Africa, while rapidly overhauling the malware it uses to break into corporate networks.
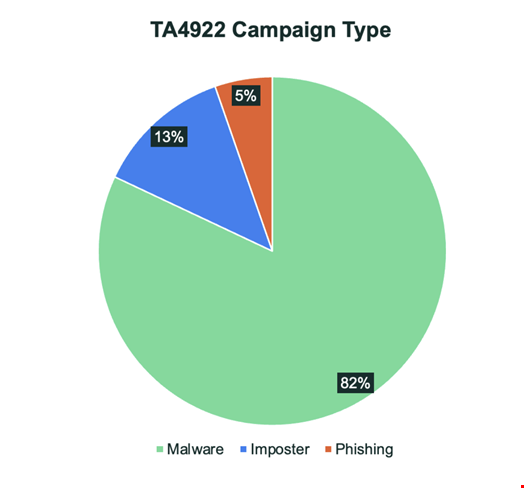
According to new analysis from Proofpoint, the actor, tracked as TA4922, is financially motivated and focused on gaining remote access to victim systems for data theft, fraud and the resale of access. The group runs more distinct campaigns than any other cybercrime actor Proofpoint currently tracks.
Its operations are unusually varied, mixing malware delivery, credential phishing and outright fraud such as credit card theft across different campaigns.
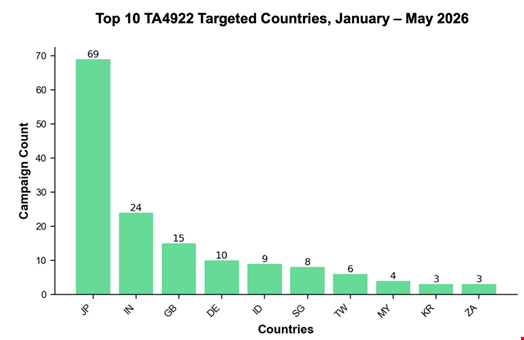
Historically concentrated on Japan, the actor also targets organizations in Taiwan, Korea, Singapore and India. In recent months its campaigns have reached the UK, Germany, Italy and South Africa.
The lures are carefully localized, impersonating tax authorities, finance departments and human resources teams in the target's own language and themed around payroll, invoicing and HR notices.
TA4922 also tries to move victims off email and onto messaging apps such as LINE, WhatsApp and Microsoft Teams, where it can continue the social engineering beyond the view of email security.
Read more on similar campaigns: Silver Fox Cyber Campaigns Show Shift Toward Dual Espionage.
The group's tooling has reportedly shifted quickly. Recent campaigns delivered a newly identified backdoor, Atlas RAT, alongside two fresh loader families Proofpoint named RomulusLoader and SilentRunLoader, in addition to long-used malware such as ValleyRAT, also known as Winos 4.0.
Payloads were typically installed through DLL sideloading and staged from consumer file-sharing services.
TA4922 also blends in with legitimate software, using RomulusLoader to drop remote management tools (RMT) such as AnyDesk. Proofpoint assessed with high confidence that the group is using large language models (LLMs) to quickly build its Python malware, citing telltale signs such as an unchanged placeholder key left in the code.
Proofpoint ties TA4922 to the same broad ecosystem as the Silver Fox and Void Arachne clusters, which other researchers have linked to espionage, but assesses it as a distinct, crime-focused group. Even so, the surveillance features in its malware, including audio, webcam and keylogging capture, could be sold to or used by espionage actors.
"The global nature of this actor shows how organizations should be aware of emerging and complex threats, regardless of geographic targeting," the company wrote. "These types of actors can quickly expand and scale their tactics to include more targets at any time."
To reduce exposure, Proofpoint urged organizations to enforce application allowlisting, monitor programs running from temporary user directories and limit local administrator rights.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。