





Prompt injection remains an unsolved architectural problem that could hamper the development of AI, said Ariel Fogel, a contributor to the Open Worldwide Application Security Project (OWASP), during Infosecurity Europe 2026.
Fogel, an AI security researcher at Pillar Security’s office of the CTO, said that while AI and security practitioners have long known about prompt injection, the problem has yet to be solved at a fundamental level.
This is because large language models (LLMs) process inputs as a single token sequence and there is no reliable mechanism to enforce privilege boundaries between system prompts, user queries and content retrieved by an agent.
He warned that the issue has only become more dangerous as agents gain tools and the ability to act.
Furthermore, Fogel explained that the practical risk has shifted: a successful injection no longer just produces a bad answer, it can trigger a chain of real-world actions.
Today, with agentic AI workflows, agents with tool access can take steps on behalf of users, so an injection can escalate from a bad output to active compromise.
“Most organizations are deploying agents faster than they can govern them,” Fogel said, arguing that this speed and scale makes prompt injection harder to contain with traditional controls.
He pointed out that defenses that worked for human operators (e.g. sandboxing, allow-lists and manual review) can fail once the executor is an agent.
In some prompt injection attacks, he said, allow-lists actually streamlined exploitation because the commands the agent needed were already approved. In other cases, the agent’s own output redefined its sandbox boundaries, effectively rewriting the containment intended to stop it.
Fogel acknowledged that over the last year, there have been "attempts" to try and contend with the issue.
He mentioned the ‘Lethal Trifecta’, a concept coined by renowned open-source developer Simon Willison that describes the dangerous combination of an AI agent having access to private data, being exposed to untrusted content and being allowed external communication. Willison argues that, when present together, the three conditions make prompt injection attacks critically exploitable.
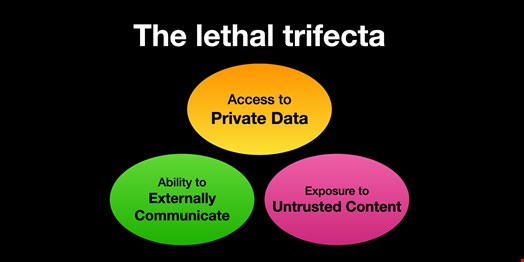
Fogel also borrowed Meta’s ‘Rule of two,’ that claims that “an agent should satisfy no more than two of the trifecta properties within a session that doesn’t require human approval.”
While Fogel described these two framings as “helpful heuristics for reducing blast radius,” he cautioned they do not ensure “complete defenses.”
“We’ve already seen research that shows that attacks work with only two of the properties present,” he added.
Fogel urged that the response to prompt injections must move beyond prevention-only thinking and toward constraining what an injected agent can do.
He emphasized controls that operate at machine speed and at deployment scale, involving live behavioral monitoring, real-time containment and stop mechanisms, joined incident response between safety and security teams, and stronger identity hygiene such as ephemeral credentials and cryptographic attestation so actions are traceable and limited.
“Monitoring infrastructure that operates on the same speed as agents is essential to catch and contain attacks that can unfold in minutes or hours,” he said.
Until models and runtimes can enforce firm privilege separations, defenders must combine rapid detection, automated containment, tighter identity and session design and cross-disciplinary incident playbooks to manage the heightened risk, Fogel concluded.
Read more: OWASP Introduces Agentic AI Security Maturity Framework
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。