





Nearly all software development teams have adopted AI coding assistants, but fewer than a third govern how the tools are used and that gap is capping the productivity AI promises.
The figures come from an independent survey of 831 software engineers and DevOps professionals carried out by the research firm UserEvidence for Black Duck in March 2026. It found 97% actively using the tools but just 30% with a fully governed approach to oversight.
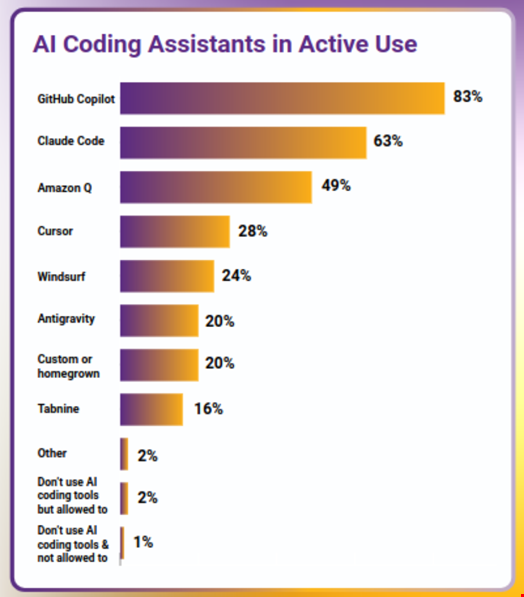
GitHub Copilot and Claude Code dominate, used by 83% and 63% of teams respectively, and most run more than one assistant.
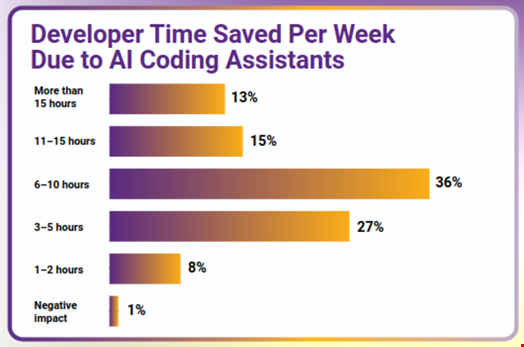
On the upside, 92% of teams credit the assistants with faster, more productive releases and on average the tools hand developers eight hours back each week.
The gains come with a catch. Nine in 10 teams hit problems with AI-generated code somewhere in their workflow, a sign the tools often shift effort downstream rather than removing it.
Most of the friction lands after the code is written:
Manual code review, cited by 52% of teams
Security testing, at 51%
Reworking the generated code, 48%
Iterating on prompts, 41%
Meanwhile, among teams whose AI-written code has surged by more than half, 57% named security testing and vulnerability fixing as the worst bottleneck.
Diana Kelley, CISO at Noma Security, warned that "faster code is not the same thing as safer code," with developer time shifting toward validating and securing what AI produces.
The teams that formalize oversight see the biggest returns. Where AI use is fully governed, 90% report a major efficiency gain, against 58% overall and 44% of teams without full governance.
However, a quarter have no defined AI coding policy at all, and although 68% called automated tracking of AI-generated code extremely important, many still flag it by hand in pull-request comments.
"AI coding assistants are no longer the challenge; governance is," said Ram Varadarajan, CEO of Acalvio, adding that AI-generated code should be treated as a new supply-chain risk fenced in by policy, secure-coding standards and human review.
Security unease rises with use. Nearly two-thirds of teams (64%) said they are moderately or extremely concerned the assistants will introduce security defects, and the heaviest users are the most worried.
Despite this, many would welcome automated help: 86% think an AI agent or model should vet AI-written code, and 56% want a dedicated AI security agent. Even so, 84% want to keep a human in the loop via pull requests or in-editor suggestions.
"Security teams need to treat AI-assisted development as part of the attack surface," warned Nicole Carignan, field CISO at Darktrace, noting that generated code can hide weak authentication, exposed secrets or over-permissioned APIs and often pulls in opaque external dependencies.
In the report, Black Duck made the same case, arguing that the teams which learn to "operationalize AI" will come out ahead, and that guardrails and shared standards are what stop the efficiency gains leaking away as work shifts to QA, DevOps and AppSec.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。