

惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

Last Week in AI
Last Week in AI
D
DataBreaches.Net
腾讯CDC
Recent Announcements
有赞技术团队
有赞技术团队
A
About on SuperTechFans
Cyber Security Advisories - MS-ISAC
Google DeepMind News
Microsoft Security Blog
云风的 BLOG
云风的 BLOG
罗磊的独立博客
月光博客
月光博客
MyScale Blog
MyScale Blog
U
Unit 42
Martin Fowler
Martin Fowler
Stack Overflow Blog
Stack Overflow Blog
T
Tailwind CSS Blog
Engineering at Meta
Engineering at Meta
N
Netflix TechBlog - Medium
G
Google Developers Blog
博客园 - 【当耐特】
D
Docker
I
InfoQ
雷峰网
雷峰网

www.infosecurity-magazine.com

Just Three Ransomware Gangs Accounted for 40% of Attacks Last Month Google Chrome Rolls Out Protection Against Infostealers Targeting Session Cookies STX RAT Targets Finance Sector With Advanced Stealth Tactics Bitcoin Depot Reports $3.6m Crypto Theft After System Breach Atomic Stealer MacOS ClickFix Attack Bypasses Apple Security Warnings Middle East Hack-for-Hire Operation Traced to South Asian Cyber Espionage Group Governance Gaps Emerge as AI Agents Drive 76% Increase in NHIs Google Warns of New Threat Group Targeting BPOs and Helpdesks Google API Keys Quietly Gain Access to Gemini on Android Devices Critical Vulnerability in Ninja Forms Exposes WordPress Sites Anthropic Launches Project Glasswing to Use AI to Find and Fix Critical Software Vulnerabilities US Thwarts DNS Hijacking Network Controlled by Russian APT28 Hackers Claude Discovers Apache ActiveMQ Bug Hidden for 13 Years Iran‑Backed Threat Actors Hit US CNI Providers via Internet‑Facing OT Assets Russian APT28 Hackers Hijack Routers to Steal Credentials, UK Security Agency Warns GPU Rowhammer Attack Enables Privilege Escalation and Full System Compromise GrafanaGhost Exploit Bypasses AI Guardrails for Silent Data Exfiltration Over $17bn Lost to Cyber Fraud in the Last Year, Warns FBI Storm-1175 Exploits Flaws in High-Velocity Medusa Attacks Fortinet Releases Emergency Patch After FortiClient EMS Bug Is Exploited New Phishing Platform Used in Credential Theft Campaigns Against C-Suite Execs New 'Storm' Infostealer Remotely Decrypts Stolen Credentials NCSC Issues Security Alert Over Hackers Targeting WhatsApp and Signal Accounts Apple Expands iOS 18 Security Updates Amid DarkSword Threat Researchers Observe Sub-One-Hour Ransomware Attacks GitHub Used as Covert Channel in Multi-Stage Malware Campaign Most CNI Firms Face Up to £5m in Downtime from OT Attacks Google Introduces Android Dev Verification Amid Openness Debate New Venom Stealer MaaS Platform Automates Continuous Data Theft Chinese Hackers Target European Governments in Espionage Campaigns
Interpol Launches Sweeping Cybercrime Crackdown in MENA R...
Kevin Poireault · 2026-05-18 · via www.infosecurity-magazine.com

International law enforcement agency Interpol has coordinated a first-of-its-kind cybercrime crackdown across the Middle East and North Africa (MENA) that led to 201 arrests.

The effort, dubbed Operation Ramz, ran from October 2025 to February 2026 across 13 countries in the MENA region.

The operation focused on neutralizing phishing and malware threats, as well as tackling cyber scams that inflict severe costs to the region.

As well as the 201 individuals arrested, Interpol and its allies identified additional 382 suspects and 3867 victims. The operation also led to the seizure of 53 servers used in cybercriminal activities.

A further set of almost 8000 pieces of data and intelligence was also disseminated among participating countries to initiate and support future investigations.
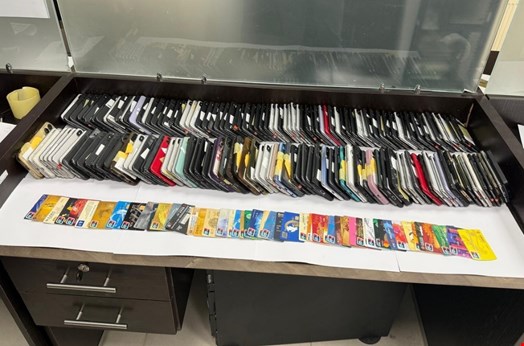
A large set of cybercrime-enabling equipment was seized during Operation Ramz. Source: Interpol

On-Site Operations in Qatar, Jordan, Oman, Algeria and Morocco

During Operation Ramz, intelligence in Qatar uncovered compromised devices that were being used by unsuspecting victims to spread threats, leading to immediate security measures and notifications to device owners.

In Jordan, police forces exposed a financial fraud scam tied to human trafficking, rescuing 15 victims who had been forced into cybercrime after having their passports confiscated.

Omani authorities also disabled a vulnerable server in a private residence that contained sensitive data, preventing further harm.

In Algeria, authorities dismantled a phishing-as-a-service operation, seizing equipment and arresting one suspect.

Moroccan authorities, meanwhile, seized devices containing banking data and phishing tools, initiating judicial proceedings against three individuals while others remain under investigation.

Public-Private Partnership

Operation Ramz involved authorities from Algeria, Bahrain, Egypt, Iraq, Jordan, Lebanon, Libya, Morocco, Oman, Palestine, Qatar, Tunisia and the United Arab Emirates.

The initiative received support from the Qatar Ministry of Interior and was partially funded by the EU and the Council of Europe under the CyberSouth+ project.

Additionally, Interpol and the participating agencies worked with several private sector partners, including Group-IB, Kaspersky, the Shadowserver Foundation, Team Cymru and TrendAI to track illegal cyber activities and identify malicious servers.

Joe Sander, CEO of Team Cymru, said his company is “proud” to have supported Interpol and the 13 countries that participated in Operation Ramz “with the visibility needed to turn data into action.”

“We will continue investing in the partnerships that protect victims and hold offenders to account,” he added.