











Just 24% of organizations test their identity disaster recovery plans every six months, according to new research which examined how businesses prepare for identity-focused cyber-attacks.
The findings suggested that despite rising investment in identity threat detection and response (ITDR), many organizations remain poorly prepared to restore critical authentication systems after a breach.
The data comes from Quest Software’s latest report, a global survey of 650 IT and security practitioners and executives. The study found that many companies place heavy emphasis on preventative controls and threat detection while neglecting response and recovery readiness.
Identity infrastructure now sits at the centre of modern IT environments, connecting users, applications, automation tools and cloud services. When attackers compromise these systems, they can quickly gain widespread access across networks, data and administrative controls.
Survey results suggested many organizations overestimate their security posture because alerts and preventative defences appear to be working. However, when identity protections fail, the speed and reliability of recovery often determine how severe the business impact becomes.
Testing identity recovery procedures remains inconsistent across many organizations, despite widespread guidance recommending regular exercises. Only a minority validate their recovery plans at least twice a year.
Survey respondents reported the following recovery testing schedules:
24% test identity disaster recovery every 6 months
44% conduct tests once a year
8% test every 2 years
24% never test their recovery plans
According to Quest Software’s report, organizations that regularly rehearse recovery tend to experience shorter outages and lower disruption during identity-related incidents.
Identity has become one of the most common entry points for cyber-attacks as organizations adopt hybrid infrastructure and cloud platforms. Systems such as Active Directory and cloud identity services manage authentication across environments, creating a critical control point for attackers.
The survey highlights particular concern around non-human identities, including service accounts and automated credentials. These identities often grow faster than governance processes can track them, leaving organizations unsure of the full scope of their identity attack surface.
More broadly, identity security challenges appear to be systemic rather than isolated to specific technologies. Respondents identified several areas that are difficult to monitor or secure:
Non-human identities (51%)
Third-party or partner accounts (49%)
Service accounts and automation credentials (47%)
On-premises identity systems and legacy environments (45%)
Privileged accounts and critical Tier 0 assets (40%)
Cloud identities (33%)
The research also found that nearly 80% of organizations remain vulnerable to identity-related threats due to complexity and insufficient tools.
Security teams are increasingly turning to automation to manage the growing volume of identity alerts and activity. The study found that 79% of respondents believe artificial intelligence can improve ITDR effectiveness by reducing alert fatigue and analysing signals across multiple identity platforms.
At the same time, ITDR adoption continues to increase. The report found that 57% of organizations now operate an ITDR programme, up from 48% the previous year, while 92% of organizations with an existing programme say they have achieved at least partial benefits.
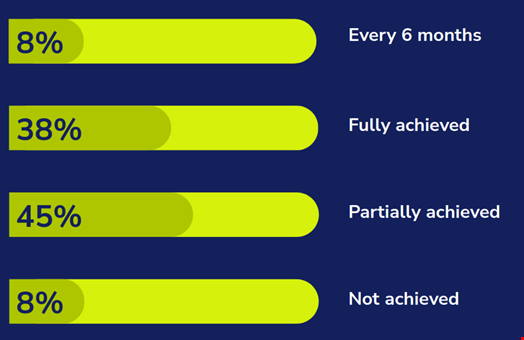
However, the report concluded that many ITDR initiatives still focus heavily on detection tools rather than a full lifecycle approach that includes identification, protection, response and recovery. Without stronger recovery testing and better visibility into identities, organizations risk remaining vulnerable when identity-driven attacks succeed.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。