


The number of zero-day vulnerabilities uncovered in enterprise software and appliances reached an all-time high last year, analysis by Google Threat Intelligence Group (GTIG) has warned.
In the report, released on March 5, GTIG said it tracked 90 zero-day vulnerabilities which were actively deployed by cyber attackers during 2025. Google defined a zero-day as “a vulnerability that was maliciously exploited in the wild before a patch was made publicly available.”
These findings are higher than the 78 zero-days tracked during 2024 but lower than the record-high of 100 zero days tracked in 2023.
Google has also warned that the way attackers use zero-days is changing and that enterprise technology is the new primary target for exploitation. 43 (48%) of zero-days identified during 2025 targeted enterprise software and appliances, up from 36 (46%) in 2024.
GTIG said that the increase “underscores the shift toward enterprise infrastructure as a structural change in the threat landscape, reflecting the value of tools that enable privilege escalation, high-level access and broad scale of impact.”
Of those zero-day exploits which targeted enterprise, almost half (21) targeted security and networking solutions. They are a prominent target for attackers, because if a zero-day in the technology can be exploited, it is useful for code execution and unauthorized access to the wider network via privileged infrastructure components.
In addition to this, security and networking appliances, including routers, switches and security appliances, often sit at the edge of the network, which can be overlooked by defenders. Attackers know this, which is why they target edge devices as they increasingly look to exploit zero-days in enterprise products.
“High-profile exploitation of enterprise tools and virtualization technologies demonstrate that attackers are deeply embedding themselves in critical business infrastructure,” said GTIG.
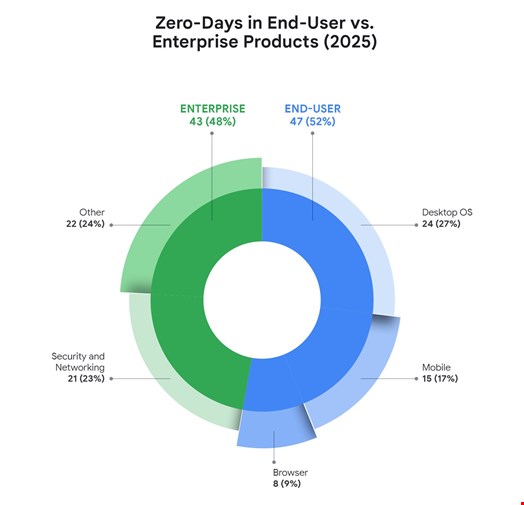
While targeting of enterprise applications is on the rise, for now, end users remain the most common target for zero-day exploitation, although the gap is closing. In 2025, 52% (47) of the tracked zero-days were used to exploit end-user platforms and products.
Of these, operating systems were the most targeted end-user product accounting for 24 (27%) of the tracked zero-days. The operating system most targeted by zero-days was Microsoft Windows.
The report pointed out that mobile operating systems saw a “notable” increase in targeting during 2025, with a total of 15 zero days in 2025 compared to the nine identified in 2024.
Meanwhile, the number of browser-based zero-day vulnerabilities tracked during the period dropped to eight (9%) in Google described as a “historical low.”
While one for reason for this is that browsers are better secured than they were previously, GTIG also suggested that attackers’ operational security has improved, which has made their activity more difficult to track, potentially reducing the volume of observed exploitation in this space.
The report also noted that during 2025, nine zero-days were linked to attacks by financially motivated threat groups, including two ransomware operations. This figure is nearly double the five zero-days attributed to financially motivated threat actors in 2024.
The report concluded that as the ongoing use of zero-day vulnerabilities by nation-state backed hacking operations - particularly those operating out of China - cybercriminal groups and others continues, defenders should be prepared for when, not if they are targeted.
“System architectures should be designed and built with ingrained security awareness, enabling inherent segmentation and least privilege access. Comprehensive defensive measures as well as response efforts require a real-time inventory of all assets to be audited and maintained,” said Google.
“While not preventative, continuous monitoring and anomaly detection, within both systems and networks, paired with refined and actionable alerting capabilities is a real-time way to detect and act against threats as they occur,” the company added.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。