

惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

大猫的无限游戏
大猫的无限游戏
MyScale Blog
MyScale Blog
雷峰网
雷峰网
量子位
小众软件
小众软件
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
博客园 - 叶小钗
T
Tailwind CSS Blog
月光博客
月光博客
博客园 - 【当耐特】
博客园_首页
罗磊的独立博客
博客园 - 三生石上(FineUI控件)
IT之家
IT之家
爱范儿
爱范儿
阮一峰的网络日志
阮一峰的网络日志
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
WordPress大学
WordPress大学
The Cloudflare Blog
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
S
SegmentFault 最新的问题
人人都是产品经理
人人都是产品经理
V
V2EX
酷 壳 – CoolShell
酷 壳 – CoolShell

www.infosecurity-magazine.com

Just Three Ransomware Gangs Accounted for 40% of Attacks Last Month Google Chrome Rolls Out Protection Against Infostealers Targeting Session Cookies STX RAT Targets Finance Sector With Advanced Stealth Tactics Bitcoin Depot Reports $3.6m Crypto Theft After System Breach Atomic Stealer MacOS ClickFix Attack Bypasses Apple Security Warnings Middle East Hack-for-Hire Operation Traced to South Asian Cyber Espionage Group Governance Gaps Emerge as AI Agents Drive 76% Increase in NHIs Google Warns of New Threat Group Targeting BPOs and Helpdesks Google API Keys Quietly Gain Access to Gemini on Android Devices Critical Vulnerability in Ninja Forms Exposes WordPress Sites Anthropic Launches Project Glasswing to Use AI to Find and Fix Critical Software Vulnerabilities US Thwarts DNS Hijacking Network Controlled by Russian APT28 Hackers Claude Discovers Apache ActiveMQ Bug Hidden for 13 Years Iran‑Backed Threat Actors Hit US CNI Providers via Internet‑Facing OT Assets Russian APT28 Hackers Hijack Routers to Steal Credentials, UK Security Agency Warns GPU Rowhammer Attack Enables Privilege Escalation and Full System Compromise GrafanaGhost Exploit Bypasses AI Guardrails for Silent Data Exfiltration Over $17bn Lost to Cyber Fraud in the Last Year, Warns FBI Storm-1175 Exploits Flaws in High-Velocity Medusa Attacks Fortinet Releases Emergency Patch After FortiClient EMS Bug Is Exploited New Phishing Platform Used in Credential Theft Campaigns Against C-Suite Execs New 'Storm' Infostealer Remotely Decrypts Stolen Credentials NCSC Issues Security Alert Over Hackers Targeting WhatsApp and Signal Accounts Apple Expands iOS 18 Security Updates Amid DarkSword Threat Researchers Observe Sub-One-Hour Ransomware Attacks GitHub Used as Covert Channel in Multi-Stage Malware Campaign Most CNI Firms Face Up to £5m in Downtime from OT Attacks Google Introduces Android Dev Verification Amid Openness Debate New Venom Stealer MaaS Platform Automates Continuous Data Theft Chinese Hackers Target European Governments in Espionage Campaigns
Citrix Urges Immediate Patching for Critical NetScaler Vu...
Kevin Poireault · 2026-03-24 · via www.infosecurity-magazine.com

Citrix has released a new critical security bulletin addressing two new vulnerabilities in its NetScaler Application Delivery Controller (ADC) and NetScaler Gateway.

The two products, formerly known as Citrix ADC and Citrix Gateway, are networking and security solutions used by enterprises to manage, optimize and secure application delivery and remote access.

CVE-2026-3055: Critical Out-of-Bounds Read

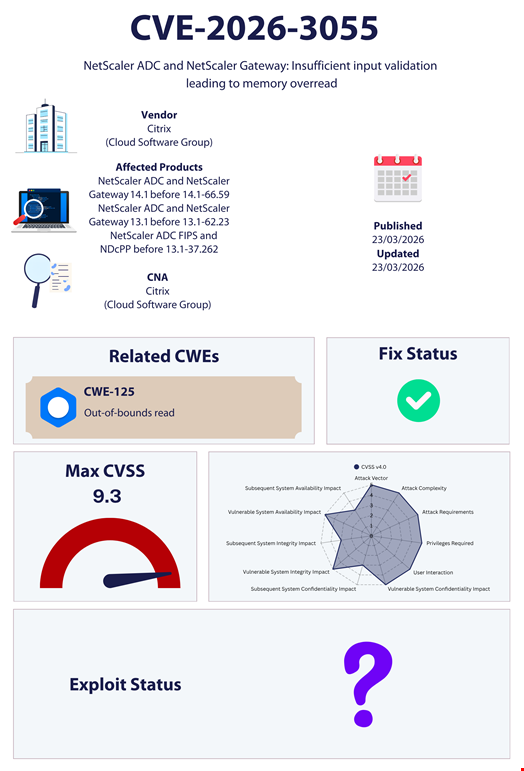
The first vulnerability, tracked as CVE-2026-3055 is a critical out-of-bounds read with a severity score (CVSS v4.0) of 9.3.

Identified internally by Citrix’s parent company, the Cloud Software Group, the flaw is due to insufficient input validation leading to memory overread. If exploited, it can enable an unauthenticated remote attacker to leak potentially sensitive information from the appliance's memory.

The products affected by CVE-2026-3055 include:

  • NetScaler ADC and NetScaler Gateway versions 14.1 before 14.1-66.59
  • NetScaler ADC and NetScaler Gateway 13.1 before 13.1-62.23
  • NetScaler ADC FIPS and NDcPP before 13.1-37.262

However, according to Citrix’s advisory, published on March 23, these vulnerabilities only affect NetScaler systems explicitly configured as a SAML Identity Provider (SAML IDP). Default or standard configurations remain unaffected.

Additionally, Citrix noted that only customer-managed instances are affected, not cloud instances managed by Citrix.

Customers can determine if they have an appliance configured as a SAML IDP Profile by inspecting their NetScaler Configuration for the specified string: “add authentication samlIdPProfile .*.”

Cloud Software Group strongly urges affected customers to install the relevant updated versions as soon as possible, which include:

  • NetScaler ADC and NetScaler Gateway 14.1-66.59 and later releases
  • NetScaler ADC and NetScaler Gateway 13.1-62.23 and later releases of 13.1
  • NetScaler ADC 13.1-FIPS and 13.1-NDcPP 13.1.37.262 and later releases of 13.1-FIPS and 13.1-NDcPP

NetScaler introduced the Global Deny List feature in its 14.1.60.52 versions. This new feature provides a method of adopting an instant-on patch to a running NetScaler without requiring a reboot.

Cloud Software Group has released Global Deny List signatures for mitigating CVE 2026-3055.

“Please note that to receive signatures meant for the Global Deny List, you must use NetScaler Console (Console On-prem with Cloud Connect or Console Service). Additionally, mitigation via Global Deny List signatures for CVE 2026-3055 is applicable only on 14.1-60.52 and 14.1-60.57 firmware builds,” the company noted.

“We recommend that you adopt fully patched builds as explained above. The Global Deny List feature is meant to be a method of quickly protecting your NetScaler so that upgrades can be done during a scheduled outage window.”

There is no known in-the-wild exploitation and no public proof-of-concept (PoC) exploit available at the time of writing.
Source: Infosecurity Magazine

CVE-2026-4368: High-Severity Race Condition Flaw

A second vulnerability, tracked as CVE-2026-4368 is a race condition flaw with a severity score (CVSS v4.0) of 7.7.

If exploited, CVE-2026-4368 can cause session mix up.

It affects NetScaler ADC and NetScaler Gateway version 14.1-66.54 if NetScaler is configured as Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy) or AAA virtual server.

Customers can determine if they have an appliance configured as one of the following by inspecting their NetScaler Configuration for the specified strings

  • An Auth Server (AAA Vserver): “add authentication vserver .*
  • A Gateway (VPN Vserver, ICA Proxy, CVPN, RDP Proxy): “add vpn vserver .*

Affected customers are advised to install NetScaler ADC and NetScaler Gateway version 14.1-66.59 to apply the patch for CVE-2026-4368.

Image credits:  JHVEPhoto / viewimage / Shutterstock.com

Read now: Salt Typhoon Uses Citrix Flaw in Global Cyber-Attack