


At this year’s Mobile World Congress in Barcelona, service providers showed up from around the world to join over 115,000 attendees from 210 countries. With more than 3,000 exhibitors, sponsors, and partners on-site, the event showcased a transformative array of technologies—from the first practical applications of 6G and industrial IoT to autonomous, unified security for an AI-native future.
Watch FNTV interview from the SOC
This marked the second year of the combined Security and Network Operations Center (S/NOC) at the world’s largest mobility and network conference. We leveraged the lessons learned from previous SOC deployments, adding the new Secure Firewall 6160, which is designed specifically for AI-ready data centers.

Cisco’s S/NOC focused on innovation, unveiling a suite of next-generation solutions, including AI-driven predictive networking and autonomous security operations. Our high-profile media announcements and live demonstrations of intelligent wireless infrastructure underscored a steadfast commitment to defining the next era of global digital communications.
The “One Cisco” strategy reached its full potential on the world stage, seamlessly unifying networking, security, observability, and Splunk’s data-driven insights to deliver unparalleled business outcomes. This holistic approach demonstrated exactly how our customers can build sovereign, AI-ready data centers, optimize hyper-distributed workplaces, and achieve total digital resilience in an increasingly complex landscape.
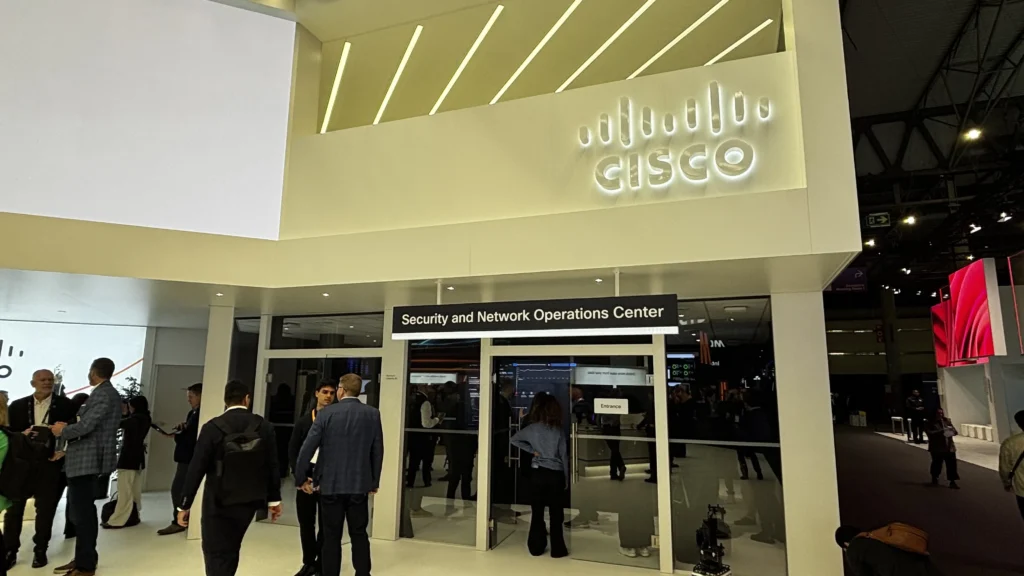
The core missions of the S/NOC at MWC 2026 were:
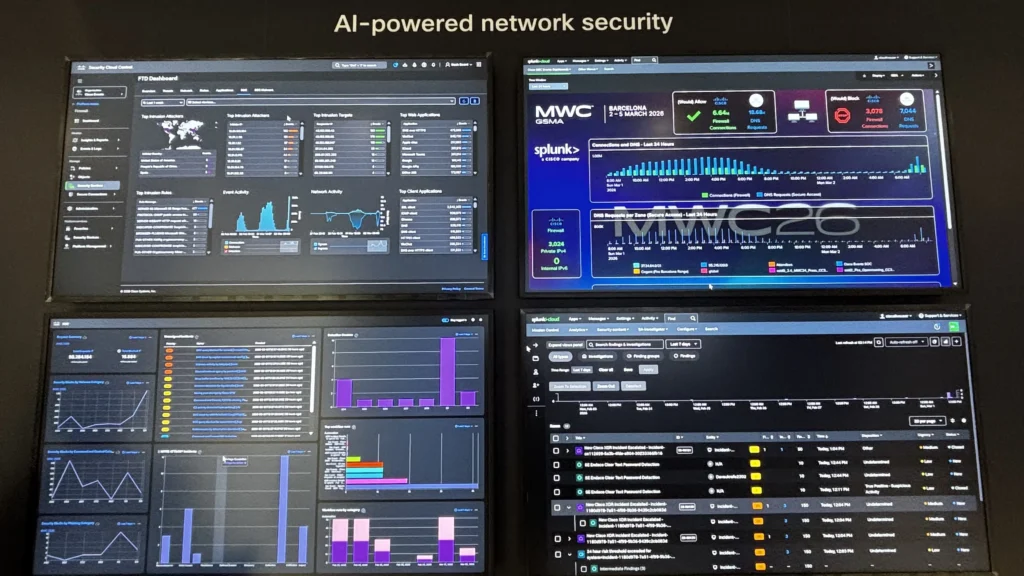
The firewall and Secure Access DNS logs were sent to Splunk Cloud as the S / NOC platform. Detections from security events were correlated in XDR for Incident generation; and Tier 1 triage / Tier 2 investigation. From hundreds of thousands of alerts, dozens of Incidents were created for investigation, ranked by priority / impact. The beta Agentic AI ‘Instant Attack Storyboard’ was used to help triage Incidents, for example this Excel file sent in the clear contained an embedded PDF file, a common way to compromise networks in a phishing attack.

The Top AI Recommendations included File Analysis for confirmation. The Tier 1 / Tier 2 analysts were empowered to pivot into Secure Malware Analytics to exam the file.

Analysis of the file determined it was not malicious but was a leak of confidential information in clear text over the network.

The analyst in XDR had the ability to complete the Incident investigation or escalate for a deeper look in Splunk Enterprise Security (ES) by a Tier 3 Threat Hunter/Incident Responder. The worklog of the XDR analyst, AI generated report and Observables (IP addresses, hash values, user data, etc.), were automatically sent to Splunk ES for Investigation, with a simple status change in XDR.

You can read more about this bi-directional integration in the blog from the SOC team at Cisco Live EMEA 2026 just two weeks prior.
Statistics are always a popular part of the SOC discussions. Below are the stats from this year’s event.

| Year | 2026 |
|---|---|
| Attendees (MWC) | 104,497 |
| Total logs captured (Splunk) | 580 million |
| Total unique devices (Firewall in Splunk) | 40,075 |
| Total logs written to cloud (Splunk) | 4.3 TBs |
| Peak bandwidth utilization (Firewall) | 3.5 Gbps |
| DNS Requests (Cisco Secure Access) | 245.5 million / 45.7k would have been blocked |
| Files sent for malware analysis (Firewall) | 5 sent to Secure Malware Analytics Files were compared to a known file database prior to submission |
Dive deeper into the innovation and technical details with the following blogs, written directly by the engineers on the ground in the MWC SOC:
Our appreciation to the engineers whose expertise made the first Mobile World Congress 2026 SNOC a success.

Network Operations Center Liaisons
Cisco Security and Splunk SOC Team
We’d love to hear what you think! Ask a question and stay connected with Cisco Security on social media.
Cisco Security Social Media
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。