




惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

V
V2EX
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
WordPress大学
WordPress大学
罗磊的独立博客
小众软件
小众软件
I
InfoQ
Y
Y Combinator Blog
宝玉的分享
宝玉的分享
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
Hugging Face - Blog
Hugging Face - Blog
MyScale Blog
MyScale Blog
博客园 - 聂微东
Microsoft Security Blog
H
Help Net Security
酷 壳 – CoolShell
酷 壳 – CoolShell
博客园_首页
S
SegmentFault 最新的问题
博客园 - 三生石上(FineUI控件)
P
Proofpoint News Feed
博客园 - 司徒正美
Cyber Security Advisories - MS-ISAC
Microsoft Azure Blog
Jina AI
Jina AI
N
Netflix TechBlog - Medium

WeLiveSecurity

Supply chain dependencies: Have you checked your blind spot? Recovery scammers hit you when you’re down: Here’s how to avoid a ‘second strike’ As breakout time accelerates, prevention-first cybersecurity takes center stage Digital assets after death: Managing risks to your loved one’s digital estate This month in security with Tony Anscombe – March 2026 edition RSAC 2026 wrap-up – Week in security with Tony Anscombe A cunning predator: How Silver Fox preys on Japanese firms this tax season Virtual machines, virtually everywhere – but not all protected Cloud workload security: Mind the gaps Move fast and save things: A quick guide to recovering a hacked account EDR killers explained: Beyond the drivers Face value: What it takes to fool facial recognition Cyber fallout from the Iran war: What to have on your radar Sednit reloaded: Back in the trenches What cybersecurity actually does for your business How SMBs use threat research and MDR to build a defensive edge Protecting education: How MDR can tip the balance in favor of schools This month in security with Tony Anscombe – February 2026 edition Mobile app permissions (still) matter more than you may think Faking it on the phone: How to tell if a voice call is AI or not PromptSpy ushers in the era of Android threats using GenAI Is Poshmark safe? How to buy and sell without getting scammed Is it OK to let your children post selfies online? Naming and shaming: How ransomware groups tighten the screws on victims Taxing times: Top IRS scams to look out for in 2026 OfferUp scammers are out in force: Here’s what you should know A slippery slope: Beware of Winter Olympics scams and other cyberthreats This month in security with Tony Anscombe – January 2026 edition DynoWiper update: Technical analysis and attribution Love? Actually: Fake dating app used as lure in targeted spyware campaign in Pakistan
ESET Research: Sandworm behind cyberattack on Poland’s po...
ESET Research · 2026-01-23 · via WeLiveSecurity

ESET Research

The attack involved data-wiping malware that ESET researchers have now analyzed and named DynoWiper

23 Jan 2026  •  , 2 min. read
ESET Research: Sandworm behind cyberattack on Poland’s power grid in late 2025

UPDATE (January 30th, 2026): For a technical breakdown of the incident affecting a company in Poland’s energy sector, refer to this blogpost.

In late 2025, Poland’s energy system faced what has been described as the “largest cyberattack” targeting the country in years. ESET Research has now found that the attack was the work of the notorious Russia-aligned APT group Sandworm.

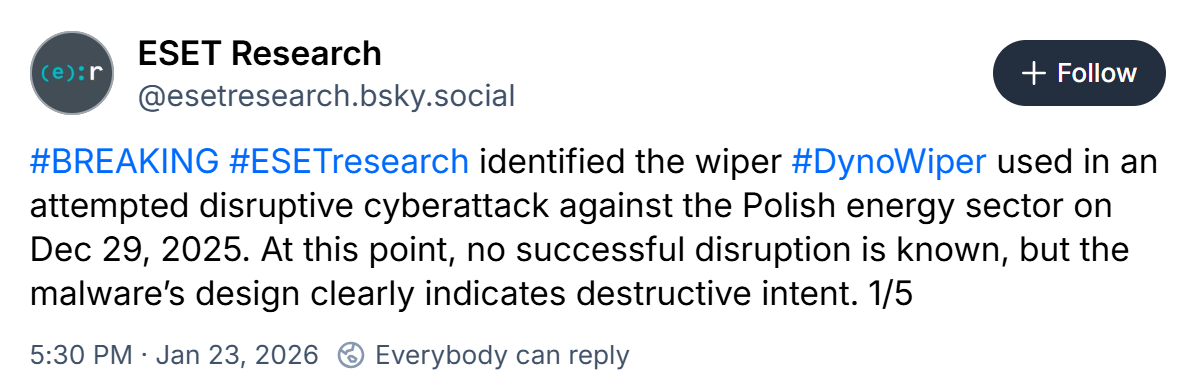
“Based on our analysis of the malware and associated TTPs, we attribute the attack to the Russia-aligned Sandworm APT with medium confidence due to a strong overlap with numerous previous Sandworm wiper activity we analyzed,” said ESET researchers. “We’re not aware of any successful disruption occurring as a result of this attack,” they added.
Screenshot 2026-01-23 200943
Source: ESET Research

Sandworm has a long history of disruptive cyberattacks, especially on Ukraine’s critical infrastructure. Meanwhile, the attack on Poland’s power grid in the last week of December involved data-wiping malware that ESET has now analyzed and named DynoWiper. ESET security solutions detect DynoWiper as Win32/KillFiles.NMO.

While details regarding the intended impact continue to be investigated, ESET researchers have highlighted the fact that the coordinated attack occurred on the 10th anniversary of the Sandworm-orchestrated attack against the Ukrainian power grid, which resulted in the first ever malware-facilitated blackout. Back in December 2015, Sandworm used the BlackEnergy malware to gain access to critical systems at several electrical substations, leaving around 230,000 people without electricity for several hours.

Fast forward a decade and Sandworm continues to target entities operating in various critical infrastructure sectors, especially in Ukraine. In their latest APT Activity Report, covering April to September 2025, ESET researchers noted that they spotted Sandworm conducting wiper attacks against targets in Ukraine on a regular basis.

For any inquiries about our research published on WeLiveSecurity, please contact us at threatintel@eset.com.

ESET Research offers private APT intelligence reports and data feeds. For any inquiries about this service, visit the ESET Threat Intelligence page.

IoCs

SHA-1 Detection Description
4EC3C90846AF6B79EE1A5188EEFA3FD21F6D4CF6 Win32/KillFiles.NMO DynoWiper.

Let us keep you
up to date

Sign up for our newsletters