
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

Y
Y Combinator Blog
The GitHub Blog
The GitHub Blog
Vercel News
Vercel News
D
DataBreaches.Net
MongoDB | Blog
MongoDB | Blog
H
Help Net Security
小众软件
小众软件
美团技术团队
T
The Blog of Author Tim Ferriss
爱范儿
爱范儿
D
Docker
Martin Fowler
Martin Fowler
大猫的无限游戏
大猫的无限游戏
博客园 - 聂微东
Blog — PlanetScale
Blog — PlanetScale
H
Hackread – Cybersecurity News, Data Breaches, AI and More
罗磊的独立博客
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
V
V2EX
S
SegmentFault 最新的问题
云风的 BLOG
云风的 BLOG
B
Blog
雷峰网
雷峰网
The Cloudflare Blog

Sansec - experts in eCommerce security

GorgonAgora: 4,800+ fake storefronts skim cards across hundreds of impersonated brands Sansec adds support for Sylius 1 & 2 Critical vulnerability in Mirasvit Cache Warmer for Magento Critical FunnelKit vulnerability threatens 40,000+ WooCommerce checkouts Composer vulnerability leaks GitHub tokens, threatens PHP supply chain Over 200 PrestaShop stores expose installer, allowing full takeover ClickFix malware hits DoD cybersecurity vendor homepage SVG Onload Tag Hides Magecart Skimmer on 99 Stores Mass PolyShell attack wave hits 471 stores in one hour Novel WebRTC skimmer bypasses security controls at $100+ billion car maker PolyShell: unrestricted file upload in Magento and Adobe Commerce Digital skimmer hits global supermarket chain Building a faster YARA engine in pure Go Magento Developers Impersonated in Targeted GitHub Malware Operation Claude finds 353 zero-days on Packagist The billion-dollar security.txt problem Keylogger targets 200,000+ employees at major US bank ConnectPOS leaked Github secrets for years Critical backdoor found in MGT Varnish extension SessionReaper attacks have started, 3 in 5 stores still vulnerable SessionReaper, unauthenticated RCE in Magento & Adobe Commerce (CVE-2025-54236) Adobe patches critical Magento admin takeover via menu injection Backdoor found in popular ecommerce components Found defunct.dat on your site? You've got a problem. You have 2 weeks left to set up CSP for your store Merchants left guessing at last-minute PCI-DSS u-turn Magento Security Release APSB25-08 [Impact Analysis] Sorry, client-side security does not work Google services abused in skimming campaigns Thousands of Adobe Commerce stores hacked in competing CosmicSting campaigns
Warning: fake Magento patch 9789 contains virus
Sansec Forensics Team · 2017-04-21 · via Sansec - experts in eCommerce security

Warning: fake Magento patch 9789 contains virus

Update May 21st: a similar phishing mail circulates about a fake patch SUPEE-1798.

Update Apr 22nd: added reference to Neutrino Bot and POS systems

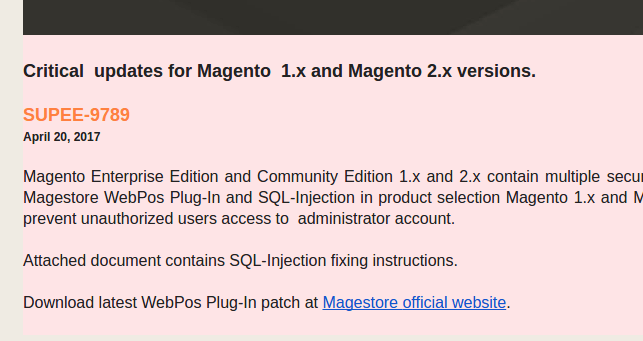
This week a mail was sent out to announce the new Magento patch SUPEE-9789. It is fake and it contains malware. There is no patch 9789. The message (full headers below) mimics an official Magento accouncement. It has two malicious payloads:

  1. An attached Word document with macro, identified as virus
  2. A request to run demo.magestore.com/webpos3/media/webpos.exe, which was identified as a new variety of the notorious Neutrino Bot (VirusTotal.

Fake #Magento patch contains malware:
Neutrino Bot aka #Kasidet, blog by @gwillem:https://t.co/o32MSYlLPx
IOCs: https://t.co/UyxSJJPEgz

— Bart (@bartblaze) April 21, 2017

This specific malware is known to target POS systems, a.k.a. cash registers. Among other things, it will harvest payment data and passwords, and enslave the cash register into a botnet that can be used for DDoS attacks.

Curiously, the malware is hosted on a server of MageStore, a legitimate vendor of POS systems. It appears that MageStore runs a vulnerable version of ProFTPd which allows anyone to upload files to their server. Unfortunately, MageStore couldn't be reached, and the malware is still on their server as of April 22nd.

Please get in touch if you have received this message as we are trying to establish the scope of intended targets. So far, we have received reports from extension vendors and hosting providers.

Thanks to Andrew Howden for additional research.

Full headers:

Return-path: <info@magestore.com>
Envelope-to: REDACTED
Received: from mail.hal-pc.org ([66.187.70.28])
 by REDACTED with esmtp (Exim 4.84_2)
 (envelope-from <info@magestore.com>)
 id 1d1OyU-0001Zw-Go
 for REDACTED; Fri, 21 Apr 2017 05:11:12 +0200
Received: from mail.hal-pc.org (localhost [127.0.0.1])
 by mail.hal-pc.org (Postfix) with ESMTP id 66AD33E8AA7E
 for <REDACTED>; Thu, 20 Apr 2017 22:11:09 -0500 (CDT)
Received: from 144.217.200.38 (unknown [5.189.203.59])
 (Authenticated sender: jstan@hal-pc.org)
 by mail.hal-pc.org (Postfix) with ESMTPA id BA8DF3E8AA7D
 for <REDACTED>; Thu, 20 Apr 2017 22:11:03 -0500 (CDT)
Message-ID: <5BA1E85F5783AD1EC2C78E3226331470@magestore.com>
From: "info@magento.com" <info@magestore.com>
To: REDACTED
Subject: Critical updates for Magento 1.x and Magento 2.x versions - SUPEE-9789
Date: Thu, 20 Apr 2017 20:11:01 -0700
Organization: Magento.com
MIME-Version: 1.0

Read more