惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
博客园_首页
雷峰网
雷峰网
Cyber Security Advisories - MS-ISAC
WordPress大学
WordPress大学
腾讯CDC
T
Tailwind CSS Blog
A
About on SuperTechFans
H
Hackread – Cybersecurity News, Data Breaches, AI and More
The GitHub Blog
The GitHub Blog
T
The Blog of Author Tim Ferriss
G
Google Developers Blog
The Cloudflare Blog
D
DataBreaches.Net
Recent Announcements
Engineering at Meta
Engineering at Meta
B
Blog
博客园 - 聂微东
阮一峰的网络日志
阮一峰的网络日志
月光博客
月光博客
博客园 - 司徒正美
MongoDB | Blog
MongoDB | Blog
Google DeepMind News
Apple Machine Learning Research

Cybersecurity Dive - Latest News

Dozens of Red Hat npm packages targeted in supply chain attack Turning tension into collaboration: How CIOs and CISOs can lead together Trump signs EO seeking early government access to powerful AI models Anthropic shares Mythos with 150 more organizations, including critical infrastructure operators Without strong governance, companies put credit ratings at risk in AI era CISA adds critical Palo Alto Networks firewall flaw to KEV as company, researchers warn of exploitation How Canva scaled to 260+M users while elevating security and productivity Top 4 data security best practices for the AI-enabled enterprise CISA urges security teams to check for software development compromises How CISOs can manage sovereign-cloud security risks IBM’s new $5B initiative will help enterprises rapidly patch open-source vulnerabilities Enterprise data is creeping its way into shadow AI tools Coordinated operation takes down Glassworm botnet Leading AI models are more vulnerable to malicious prompts than vendors claim Iranian government, not hacktivist group, breached LA Metro system, security firm says FBI warns about PhaaS platform used to access Microsoft 365 environments Iran-linked hackers target key US, allied sectors with sophisticated spear-phishing messages New York regulator calls for additional cyber mitigation amid heightened threat environment CISA asks cybersecurity community to alert it to vulnerability exploitation Grafana Labs links GitHub environment breach to TanStack npm supply chain attack 7-Eleven hit by data breach Microsoft disrupts cybercrime operation that hid behind legitimate software Compromised coding tool helped hackers breach thousands of GitHub repositories Telecom sector launches its own private ISAC Patch bypass allows hackers to exploit prior flaw in SonicWall SSL-VPN Grafana Labs says hacker gained access to codebase through leaked token How a government contest launched a revolution in AI-based bug hunting Attackers exploit critical flaw in Cisco Catalyst SD-WAN Controller MSPs need AI to fight AI-fueled cyberthreats: Guardz More money is going to physical security, but it’s often CISOs that oversee it: EY
White House questions tech industry on defensive AI use, ...
Eric Geller · 2026-05-02 · via Cybersecurity Dive - Latest News

An article from site logo

Companies may be reluctant to answer some of the government’s questions, given the sensitive topics they address.

Published May 1, 2026

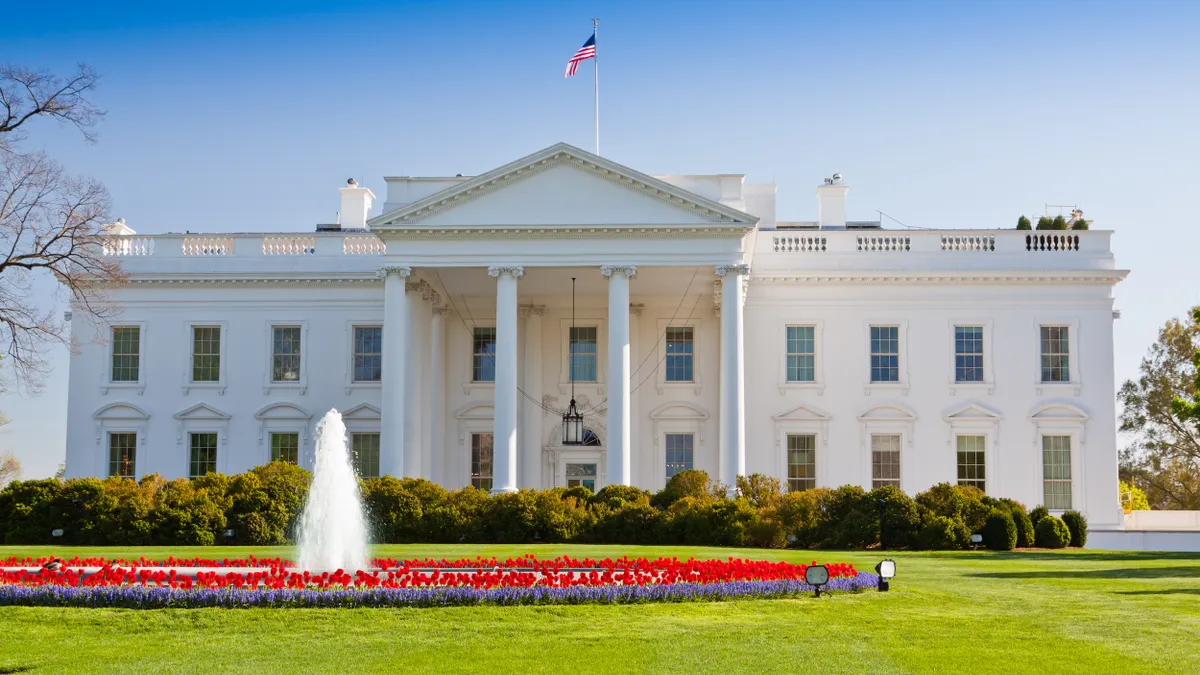
View of the White House with flowers and fountain in front.

The North Portico of the White House is seen in Washington, D.C. The Trump administration recently asked tech companies for information about their cybersecurity practices and AI use. Getty Images

The U.S. government wants to know how major U.S. technology companies are using AI to protect their computer networks and how they’re preparing for the possibility of an AI-driven cybersecurity crisis.

Officials from the White House’s Office of the National Cyber Director (ONCD) have reached out to tech giants in recent weeks with questions about AI, information sharing, vulnerability patching and how the federal government can help, according to an email and a list of questions shared with Cybersecurity Dive.

“The White House continues to proactively engage across government and industry to address several Al/cybersecurity priorities,” Jennifer Belair, the assistant national cyber director for external affairs, said in the April 23 email. “This includes working with frontier AI labs to discuss opportunities for collaboration, as well as shared approaches and protocols to address the challenges associated with scaling this technology. We are grateful for your collaboration to date and believe that your organization has the capabilities and expertise to ensure the United States and Americans are protected.”

ONCD asked the companies to answer 11 questions on a range of cybersecurity topics by May 1.

A few of the questions are straightforward, such as “Are you currently using Al detection and response tools and services?” and “How are Al models or platforms integrated into your software stack?” But most of the questions are more complicated, such as how quickly companies can identify and fix known vulnerabilities and what barriers they face to improving their cyber posture.

Still other questions involve sensitive internal details that companies are unlikely to share. One question asks for a list of the networks, hardware and software that are critical to companies’ continuity of operations, as well as a description of how the companies isolate those systems from their traditional business networks. Another question asks the companies to describe what would happen if their most critical systems were compromised.

The White House also asked the companies what information-sharing mechanisms they use and whether those processes have gaps; whether the companies have any recommendations for improving coordination with state and local governments; and what is “the most helpful role the federal government can play here,” citing as an example a “public-private consortium structure that delivers operational value.”

The email did not include a list of recipients, making it unclear which companies received it. ONCD did not respond to multiple requests for comment about the outreach. The White House appears to have sent different questions to different stakeholders; Politico, which first reported on the outreach, quoted different language in the questions.

The outreach follows an April 28 meeting between White House cybersecurity officials and tech industry representatives about the dangers and opportunities posed by powerful new AI models.