惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

博客园 - 叶小钗
Cyber Security Advisories - MS-ISAC
Microsoft Security Blog
罗磊的独立博客
大猫的无限游戏
大猫的无限游戏
美团技术团队
让小产品的独立变现更简单 - ezindie.com
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
aimingoo的专栏
aimingoo的专栏
腾讯CDC
WordPress大学
WordPress大学
Apple Machine Learning Research
F
Fortinet All Blogs
G
Google Developers Blog
MongoDB | Blog
MongoDB | Blog
Microsoft Azure Blog
小众软件
小众软件
Engineering at Meta
Engineering at Meta
博客园_首页
B
Blog RSS Feed
D
Docker
M
MIT News - Artificial intelligence
爱范儿
爱范儿
I
InfoQ

Cybersecurity Dive - Latest News

Dozens of Red Hat npm packages targeted in supply chain attack Turning tension into collaboration: How CIOs and CISOs can lead together Trump signs EO seeking early government access to powerful AI models Anthropic shares Mythos with 150 more organizations, including critical infrastructure operators Without strong governance, companies put credit ratings at risk in AI era CISA adds critical Palo Alto Networks firewall flaw to KEV as company, researchers warn of exploitation How Canva scaled to 260+M users while elevating security and productivity Top 4 data security best practices for the AI-enabled enterprise CISA urges security teams to check for software development compromises How CISOs can manage sovereign-cloud security risks IBM’s new $5B initiative will help enterprises rapidly patch open-source vulnerabilities Enterprise data is creeping its way into shadow AI tools Coordinated operation takes down Glassworm botnet Leading AI models are more vulnerable to malicious prompts than vendors claim Iranian government, not hacktivist group, breached LA Metro system, security firm says FBI warns about PhaaS platform used to access Microsoft 365 environments Iran-linked hackers target key US, allied sectors with sophisticated spear-phishing messages New York regulator calls for additional cyber mitigation amid heightened threat environment CISA asks cybersecurity community to alert it to vulnerability exploitation Grafana Labs links GitHub environment breach to TanStack npm supply chain attack 7-Eleven hit by data breach Microsoft disrupts cybercrime operation that hid behind legitimate software Compromised coding tool helped hackers breach thousands of GitHub repositories Telecom sector launches its own private ISAC Patch bypass allows hackers to exploit prior flaw in SonicWall SSL-VPN Grafana Labs says hacker gained access to codebase through leaked token How a government contest launched a revolution in AI-based bug hunting Attackers exploit critical flaw in Cisco Catalyst SD-WAN Controller MSPs need AI to fight AI-fueled cyberthreats: Guardz More money is going to physical security, but it’s often CISOs that oversee it: EY
‘Fundamental tension’ undermines manufacturers’ cybersecu...
Eric Geller · 2026-04-28 · via Cybersecurity Dive - Latest News

An article from site logo

Dive Brief

A simple security mistake caused roughly one-quarter of all financial losses in the sector in 2025, cybersecurity insurer Resilience said.

Published April 28, 2026
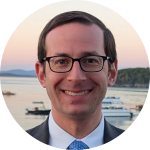
Two people standing face to face on a plastics production line.

Two workers standing face to face on a production line in a plastics factory. Manufacturers are struggling with cybersecurity, despite being some of the most targeted infrastructure operators, a new report found. Getty Images

Dive Brief:

  • The manufacturing sector is woefully unprepared to defend against cyberattacks, even as it was the most targeted community in 2025, accounting for one in four attacks, cybersecurity insurance firm Resilience said in a report published on Tuesday.
  • Several factors make it difficult for manufacturers to upgrade their cybersecurity defenses, including the cost of downtime, according to the report.
  • Even so, the threat picture is dire: Ransomware attacks on manufacturers increased significantly more in 2025 than the average growth rate across all sectors.

Dive Insight:

Manufacturing firms face “a fundamental tension” that impedes their cybersecurity progress, according to Resilience: “The perceived risk of taking production offline to implement security controls often feels greater than the risk of operating without them.” At the same time, automation and remote access have become much more common in the industry, particularly in the wake of the COVID-19 pandemic, when remote system management became the norm for public-health reasons.

As the attack surface has grown, attackers have matured. Ransomware groups increasingly operate through an affiliate model that lowers the barrier of entry for destructive but low-skilled attackers, Resilience said. In addition, cybercriminals eagerly capitalize on manufacturers’ “low tolerance for downtime” and tight security budgets. Government-backed hacking groups also frequently target manufacturers to undermine national security preparedness and steal intellectual property.

Ransomware attacks increased by roughly 46% overall between January and September 2025 compared to the same period in 2024, but they increased by 61% in the manufacturing sector, Resilience said, citing data from the threat intelligence firm KELA.

While state-sponsored espionage poses national-defense concerns, ransomware is by far the most serious threat to manufacturers’ bottom lines. Ransomware accounted for 90% of losses in the sector between March 2021 and February 2026, according to Resilience — despite representing only 12% of insurance claims by the firm’s policyholders.

Manufacturers’ security weaknesses aren’t uniquely complex. The single costliest weakness, according to the report, is multifactor authentication (MFA) misconfiguration. Poorly configured MFA caused roughly one-quarter of all losses, and nearly 10% of losses stemmed from a complete lack of MFA. “These are fixable problems with outsized financial consequences,” Resilience said.

By contrast, the exploitation of software vulnerabilities accounted for only roughly 13% of losses over the same five-year period, concentrated in several high-profile ransomware attacks by groups such as Black Basta.

Resilience encouraged manufacturers to carefully verify their MFA deployments, improve their vulnerability tracking and mitigation processes, tighten restrictions on financial transfers and enforce security requirements on their vendors.