
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

WordPress大学
WordPress大学
A
About on SuperTechFans
量子位
B
Blog RSS Feed
让小产品的独立变现更简单 - ezindie.com
博客园_首页
MongoDB | Blog
MongoDB | Blog
小众软件
小众软件
Blog — PlanetScale
Blog — PlanetScale
Microsoft Azure Blog
V
V2EX
Google DeepMind News
Cyber Security Advisories - MS-ISAC
H
Hackread – Cybersecurity News, Data Breaches, AI and More
G
Google Developers Blog
U
Unit 42
D
DataBreaches.Net
博客园 - Franky
D
Docker
宝玉的分享
宝玉的分享
Y
Y Combinator Blog
月光博客
月光博客
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
Hugging Face - Blog
Hugging Face - Blog

Palo Alto Networks Blog

Palo Alto Networks Named a Leader in the 2026 Gartner® Magic Quadrant™ for Hybrid Mesh Firewall Secure AI Coding: Governing every agent, artifact, and identity Building Securely From Day One: Palo Alto Networks Partners with the Zendesk Startup Program Making the Most of the Cloud Marketplace Opportunity Celebrating excellence: Palo Alto Networks announces the 2026 North America Partner of the Year Awards Unit 42 Defends Organizations Against Next-Gen Frontier AI Risks with Anthropic’s Mythos 5 Putting OpenAI Cyber Models to Work for Defenders Palo Alto Networks Recognized as the Only Vendor to be Named a 4X Leader in SASE and SSE Gartner Magic Quadrant Reports Strengthening Security of AI Coding: Prisma AIRS API Integration with OpenAI Codex Bridging the Gap: An Unprecedented Approach to Browser and Endpoint Security Prisma AIRS - Unified Data Protection for Claude Redefining Network Security for the Frontier AI Era Introducing Unit 42 Threat Intelligence: Know What Matters, Understand the Adversary, and Act Faster Palo Alto Networks Achieves Global CBPR and PRP Certifications Announcing the General Availability of Prisma AIRS AI Gateway Palo Alto Networks and AT&T - Delivering Quantum-Resilient SASE Fabric What It Takes to Secure Claude Cowork Across the AI Enterprise It Might Feel Like We’ve Been Here Before, But We Haven’t A Defining Moment in Identity Security New Executive Order Accelerates Post-Quantum Readiness Amid the Cryptographic Reset Built to Last: What Stonehenge Teaches us About IT Architecture & Cyber Resilience Expanding Our Footprint: Local Cloud Availability for Prisma AIRS in Japan The Invisible CEO of Crisis: Breaking the Cycle of CISO Burnout Securing the Agentic AI Frontier: Palo Alto Networks and Databricks Deliver a New Standard for AI Security Securing Canada’s Digital Future: Why PBMM Matters Beyond Government Beyond Human Oversight: Adapting to the Frontier AI Era Shifting from Data Hoarding to Active Defense: Navigating the New Era of OMB M-26-14 European Digital Sovereignty Starts With Trust How AI and Evasion Demand a Radical Shift in Network Threat Prevention Reinventing Security for the Agentic NVIDIA AI Factory
Closing the Gap by Enhancing Visibility and Mitigating Risks
Viv Danks · 2026-04-01 · via Palo Alto Networks Blog

In the race to digitise public services, the UK’s digital estate has grown into a vast, borderless ecosystem that manual audits can no longer track. For UK Government departments, local authorities and NHS trusts, it is a sprawling, shifting landscape of cloud workloads, legacy infrastructure, shadow IT and third-party supplier connections.

This complexity creates blind spots that modern threats exploit. Recognising this vulnerability, the UK Government is moving toward a secure-by-design digital infrastructure, with the 2026 Government Cyber Action Plan (GCAP) setting a high bar for resilience. A central theme of the GCAP is the urgent need for the government to have better visibility of cyber security and resilience risk. Fundamentally, organisations cannot secure what they cannot see. As the GCAP explicitly states, the Government will use “data sources from across the government to truly understand government-wide and departmental cyber risks.”

The Challenge: Visibility in a “Landscape”

Many public sector organisations rely on a complex web of spreadsheets, data calls, legacy tools and manually curated lists to create an inventory of their internet-connected assets. But attackers do not look at an organisation's internal lists; they scan the internet for what they have forgotten to secure. Whether it is an unpatched server from a legacy project or a misconfigured database in a department, these "unknown unknowns" are the primary entry points for attackers.

The Strategic Mission: Empowering the Public Sector and Critical Industries

Palo Alto Networks Cortex Xpanse® is an active external attack surface management (EASM) solution that provides an outside-in view of organisations' entire digital footprint. It helps leaders meet national resilience goals:
  • Comprehensive, Continuous Visibility: Xpanse scans the global internet space continuously and identifies every asset associated with an organisation, without requiring software agents to be installed on your systems.
  • Accelerate Response: Leveraging automation, the solution streamlines response processes and enhances collaboration across dispersed teams from the sharing of findings to tracking actions and remediation.
  • Supply Chain Integrity: Inline with the new Cyber Security and Resilience Bill (bringing managed service providers and critical third parties into scope), Xpanse allows organisations to assess the internet-facing security posture of third-party partners and suppliers, ensuring a weak link elsewhere doesn't compromise the broader mission.
  • Alignment with GovAssure: Xpanse provides a consolidated risk profile and inventory for all internet-facing and cloud assets required for GovAssure assessments, turning a manual, months-long audit process into a continuous, data-driven cycle.
  • Investment prioritisation: Xpanse provides that much needed visibility to help executive committees and boards prioritise investment decisions on legacy IT and technical debt.

Aligning to National Cybersecurity Centre (NCSC) Guidance

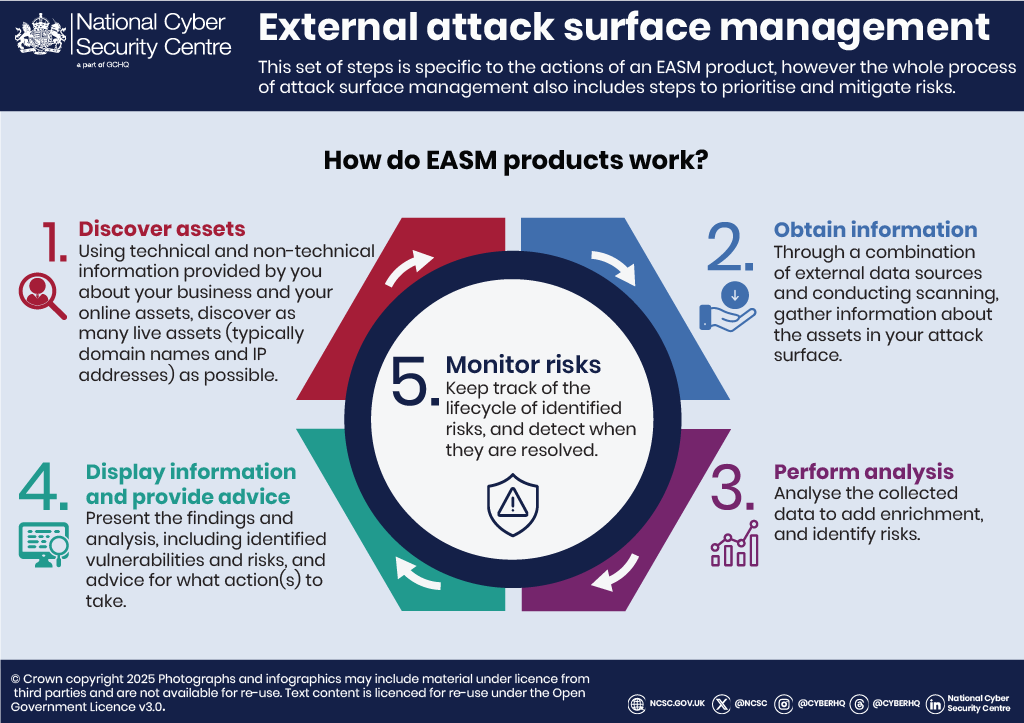
How external attack surface management products work.

Palo Alto Networks Cortex Xpanse aligns with the National Cyber Security Centre (NCSC) external attack surface management (EASM) buyer's guide by providing automated discovery, continuous monitoring and risk prioritisation of internet-facing assets. It replaces manual, point-in-time audits with a proactive, agentless solution. By automating the discovery of all internet-accessible assets (including shadow IT and unmanaged cloud operations) the platform fulfills the NCSC’s core requirement for continuous global monitoring and rapid attribution. This data-driven approach allows for the automated prioritisation of critical exposures, such as RDP, and integrates seamlessly with multiple third-party automation and visualisation tools, including Cortex XSOAR® and XSIAM, to accelerate remediation with national incident response standards.

In fact, with Palo Alto Networks deployment of Cortex Xpanse, we were able to achieve a 95% reduction in external vulnerability management spending across more than 700,000 cloud instances, while improving coverage and outcomes.

Palo Alto Networks Cortex Xpanse Capabilities
  • Discover Assets: Leveraging organisations' known asset inventory and other data points, Xpanse performs continual, automated discovery of all internet-accessible assets, effectively eliminating blind spots created by shadow IT and unmanaged cloud operations.
  • Obtain Information: Always-on, continuous monitoring of an organisation's entire attack surface through daily scans of the global IP address space, ensuring that newly exposed services are identified quickly and accurately.
  • Perform Analysis: Xpanse automates and prioritises alerts on all identified risks by severity, enabling organisations to optimise resolution and risk management, allowing teams to properly allocate resources and focus on the most critical risks to the organisation.
  • Display Information and Provide Advice: Leveraging a unified view of the internet facing and cloud-based estate, Xpanse provides specific resolver guidance for every identified issue, supporting and monitoring automated resolution through multiple native integrations.
  • Monitor Risk: Always on, discreet continual monitoring provides an independent real time status of the digital estate. Leveraging the threat intelligence capabilities of Palo Alto Networks, Xpanse is uniquely positioned to provide rapid coverage for newly discovered vulnerabilities, exploits or misconfigurations.

Securing the public sector requires a move from manual, point in time assessments to data-driven intelligence. Cortex Xpanse provides the foundations to remove blind spots, secure the supply chain and prevent unknown vulnerabilities in the face of sophisticated threats.

For further information and case studies, visit the links below, or schedule a demo.

  • Palo Alto Networks: Slash false positives, remediation time budget with Cortex attack surface management.
  • U.S. Pentagon: Palo Alto Networks Cortex Xpanse supercharge the Cyber Defences for the Department of Defense.
  • Accenture: Secure rapid growth with Cortex Xpanse.