


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

N
Netflix TechBlog - Medium
IT之家
IT之家
博客园_首页
Hugging Face - Blog
Hugging Face - Blog
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
美团技术团队
小众软件
小众软件
博客园 - 叶小钗
WordPress大学
WordPress大学
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
博客园 - 三生石上(FineUI控件)
罗磊的独立博客
博客园 - Franky
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
Last Week in AI
Last Week in AI
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
有赞技术团队
有赞技术团队
T
Tailwind CSS Blog
宝玉的分享
宝玉的分享
博客园 - 【当耐特】
月光博客
月光博客
Cyber Security Advisories - MS-ISAC
酷 壳 – CoolShell
酷 壳 – CoolShell
人人都是产品经理
人人都是产品经理

VMware Blogs

Diagnostics for VMware Cloud Foundation (VCF) 9.1 with Old Versions of VCF Components Mastering Infrastructure Policies in VMware Cloud Foundation Automation 9.1 Modernizing the Private Cloud: Why VCF 9.1 Lifecycle Management is a Game Changer Announcing the VMware Cloud Foundation 9.1 Upgrade Planning Tool VCF Breakroom Chats Episode 86 – Containers Made Easy: The New “Container-as-a-Service” in VCF 9.1 Securing Your VCF 9.1 Infrastructure with the Symantec Identity Security Platform Virtually Speaking: The AI Reality Check with Dave Linthicum Zero Touch Provisioning: Activating Edge Sites with VMware Cloud Foundation Edge 9.1 VCF Breakroom Chats Episode 85 – Cloning Success at Scale: Inside VCF 9.1’s App Stack Formation VMware Cloud on AWS の使用状況を確認できる API Unlocking the Full Potential of Programmable Infrastructure with VMware Cloud Foundation 9.1 – New Features and Capabilities Smarter Patching at Scale: Vulnerability Assessment and Remediation with VMware Tanzu Platform Encrypted vMotion Offload to Intel QAT in VMware Cloud Foundation 9.1 Deepen Your Expertise: Four Key Benefits of Attending Increase Deployment Flexibility with VCF Edge Automation 1.0.3 Avi Advantage: Automating Certificate Management of VCF Workloads More Memory, Less Effort: Configuring Memory Tiering in VCF 9.1 VCF 9.1 Licensing: Programmatic, Centralized, and Built to Scale Why APJ Networking Professionals Need Private Cloud Expertise VCF 9.1 Networking: Simpler VPC Connectivity Control VCF 9.1 Networking: Exploring Network Services for Virtual Private Clouds VCF Networking 9.1: Seamless DDI Integration with Infoblox The Open Source Advantage: Building from Source for Ultimate Security Expand Shared VMDKs with Clustered Applications in VMware vSAN for VCF 9.1 Monetizing Zero-Trust Security with VCF 9.1 and VMware vDefend VMware vSAN Protection and Recovery Enhancements for VCF 9.1 Deliver Production SQL Server DBaaS with VMware Data Services Manager 9.1 Maximizing Profitability: VCF 9.1 Cost-Focused Approach for VMware Cloud Service Providers Modernizing Your Infrastructure: Introducing VMware Cloud Foundation 9.1 to VCSPs VCF 9.1 is Available: Explore the New Features in Hands-on Labs
Bridging the (.Local) Gap: A Split-Domain Design for VMwa...
vmwareblogs · 2026-04-17 · via VMware Blogs

In the ever-evolving landscape of private cloud, technical debt often hides in the most fundamental places, like your DNS naming convention. For many years, .local was the go-to Top-Level Domain (TLD) for internal Active Directory environments.

However, as per RFC 6762, .local is now officially reserved for Multicast DNS (mDNS) and is no longer recommended for unicast DNS in enterprise environments. As we evolve VMware Cloud Foundation (VCF), we are implementing stricter guardrails to align with these global standards, encouraging a shift toward valid, routable, or non-conflicting TLDs.

The Challenge: The Hardening of VCF

-5As part of our commitment to platform security and stability, we have begun “hardening” the VCF stack. This means that several modern components are losing support for .local TLDs to prevent resolution conflicts and security vulnerabilities.z

Where .local is no longer supported:

  • VCF Identity Broker (VIDB): The modern authentication backbone for VCF 9.x.
  • VCF Automation: Modern cloud management capabilities
  • vSphere Supervisor: Essential for Kubernetes consumption and modern application delivery

Where .local is still supported (for now):

To provide a transition window, core infrastructure components still allow .local configuration:

  • VCF Operations
  • vCenter Server
  • VCF Networking (NSX)
  • SDDC Manager

Design Scenario: The Transition Strategy

We understand that migrating an entire enterprise’s DNS infrastructure is not an overnight task. If your core VCF components (vCenter, NSX, SDDC Manager) are already tied to a .local domain and you aren’t ready for a full-scale rename, you need a hybrid DNS design to consume modern VCF services.

To bridge the gap, we recommend a “Transition Zone” approach. While your core management components stay on .local, you must introduce a standard-compliant TLD (e.g., corp.vcf.com or vcf.internal or Green.NET) for the modern services you wish to deploy.
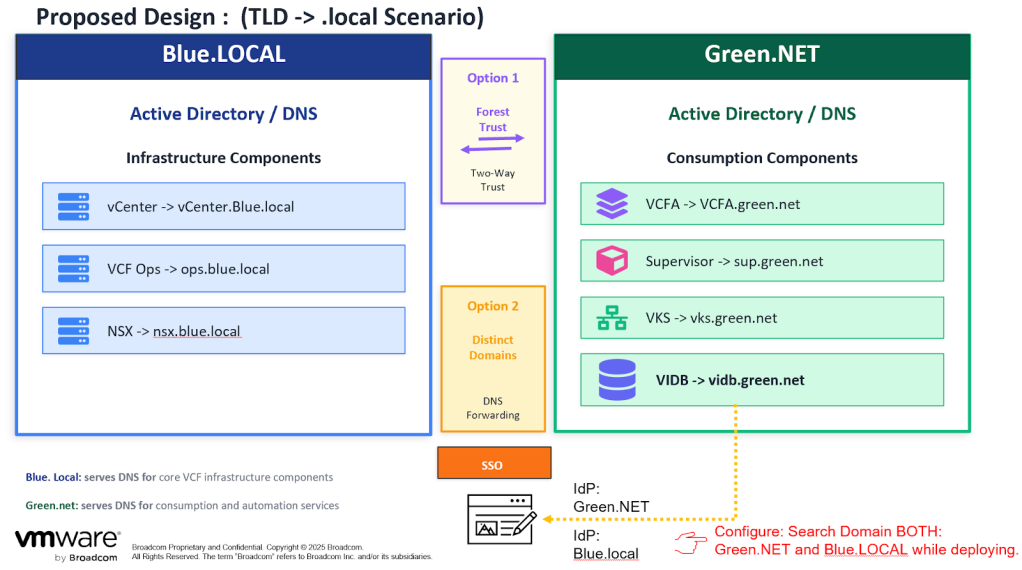
The proposed design addresses the challenge of modernizing a VMware Cloud Foundation (VCF) environment that still relies on a legacy .local Top-Level Domain (TLD). Because modern components are increasingly “hardened” against the use of .local due to RFC standards, this design implements a split-domain architecture to bridge the gap between legacy core infrastructure and modern consumption services.

Split-Domain Architecture

The design divides the environment into two distinct logical zones based on their technical requirements and supportability:

  • Legacy Infrastructure Zone (Blue.LOCAL): This zone serves the core VCF infrastructure components that still support .local for backward compatibility.
    • vCenter Server: vCenter.Blue.local
    • VCF Operations: ops.Blue.local
    • NSX Manager: nsx.Blue.local
  • Modern Consumption Zone (Green.NET): This zone utilizes an RFC-compliant TLD for newer services where .local is strictly unsupported.
    • VCF Automation (VCFA): VCFA.green.net
    • Supervisor / VMware vSphere Kubernetes Service (VKS): sup.green.net or vks.green.net
    • VCF Identity Broker (VIDB): vidb.green.net

Implementation Options for Interoperability

To allow these two zones to communicate and function as a unified platform, the design proposes two primary integration methods:

FeatureOption 1: Forest TrustOption 2: Distinct Domains
ConnectivityEstablishes a Two-Way Forest Trust between Blue.LOCAL and Green.NET.Maintains domains as completely Distinct Entities.
DNS StrategyShared identity and DNS records across the forest.Utilizes DNS Forwarding to resolve queries between the two domains.

Critical Configuration Requirements

To ensure successful deployment and Single Sign-On (SSO) functionality, the following configuration guardrails must be followed:

  • Identity Provider (IdP) Alignment: The SSO configuration must recognize both Green.NET and Blue.local as valid Identity Providers to allow users from either domain to access the platform.
  • Search Domains: While deploying components, it is mandatory to configure both Green.NET and Blue.LOCAL in the DNS search domain list. This ensures that services in the modern zone can correctly locate and communicate with the legacy core infrastructure.

Implementation Steps

  1. Maintain the Core: Keep your existing VCF Operations, vCenter, NSX and SDDC Manager on the .local domain to avoid disruptive renames.
  2. Establish a New Domain: Create a new, RFC-compliant DNS domain (such as .net or .internal) in your environment.
  3. Deploy Modern Services to the New Zone: When deploying VIDB, VCF Automation or vSphere Supervisor, use the new FQDNs.
  4. Cross-Zone Resolution: Ensure that your DNS servers can resolve both the legacy .local zone and the new modern zone to allow inter-component communication.

For this hybrid design to function correctly, two specific configuration steps are mandatory during deployment:

  1. Dual Search Domains: When deploying any component (especially in the Green.NET zone), you must configure BOTH Green.NET and Blue.LOCAL in the DNS search domain list. This ensures that a modern service like VKS can find the legacy vCenter it depends on.
  2. Unified SSO Identity: The Identity Provider (IdP) must be configured to recognize both the Green.NET and Blue.local domains. This allows users from both domains to authenticate into each component.

This split-domain design offers a strategic pathway for VCF customers to adopt new capabilities and features without the immediate, costly burden of a full-scale .local domain migration. By leveraging a dual-zone architecture and essential cross-domain configuration, enterprises can ensure platform stability, security compliance, and access to all next-generation VCF capabilities today.


Discover more from VMware Cloud Foundation (VCF) Blog

Subscribe to get the latest posts sent to your email.