

惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

酷 壳 – CoolShell
酷 壳 – CoolShell
G
Google Developers Blog
L
LangChain Blog
Y
Y Combinator Blog
Vercel News
Vercel News
WordPress大学
WordPress大学
大猫的无限游戏
大猫的无限游戏
博客园 - Franky
V
Visual Studio Blog
小众软件
小众软件
月光博客
月光博客
A
About on SuperTechFans
H
Hackread – Cybersecurity News, Data Breaches, AI and More
T
The Blog of Author Tim Ferriss
有赞技术团队
有赞技术团队
M
MIT News - Artificial intelligence
阮一峰的网络日志
阮一峰的网络日志
Last Week in AI
Last Week in AI
博客园 - 【当耐特】
让小产品的独立变现更简单 - ezindie.com
MongoDB | Blog
MongoDB | Blog
Jina AI
Jina AI
美团技术团队
量子位

Simon Willison's Weblog

Release: datasette 1.0a29 Thoughts on GitLab’s workforce reduction A quote from James Shore Your AI Use Is Breaking My Brain TIL: Using LLM in the shebang line of a script Learning on the Shop floor A quote from New York Times Editors’ Note A quote from Andrew Quinn A quote from Luke Curley Release: llm-gemini 0.31 Tool: Big Words Notes on the xAI/Anthropic data center deal Tool: GitHub Repo Stats Live blog: Code w/ Claude 2026 Vibe coding and agentic engineering are getting closer than I’d like Release: datasette-referrer-policy 0.1 Release: datasette-llm 0.1a7 Release: llm-echo 0.5a0 Granite 4.1 3B SVG Pelican Gallery A quote from Andy Masley April 2026 newsletter Research: TRE Python binding — ReDoS robustness demo Tool: Redis Array Playground A quote from Anthropic Sightings iNaturalist Sightings Codex CLI 0.128.0 adds /goal Our evaluation of OpenAI's GPT-5.5 cyber capabilities Quoting Andrew Kelley We need RSS for sharing abundant vibe-coded apps
Behind the Scenes Hardening Firefox with Claude Mythos Pr...
2026-05-08 · via Simon Willison's Weblog

7th May 2026 - Link Blog

Behind the Scenes Hardening Firefox with Claude Mythos Preview (via) Fascinating, in-depth details on how Mozilla used their access to the Claude Mythos preview to locate and then fix hundreds of vulnerabilities in Firefox:

Suddenly, the bugs are very good

Just a few months ago, AI-generated security bug reports to open source projects were mostly known for being unwanted slop. Dealing with reports that look plausibly correct but are wrong imposes an asymmetric cost on project maintainers: it’s cheap and easy to prompt an LLM to find a “problem” in code, but slow and expensive to respond to it.

It is difficult to overstate how much this dynamic changed for us over a few short months. This was due to a combination of two main factors. First, the models got a lot more capable. Second, we dramatically improved our techniques for harnessing these models — steering them, scaling them, and stacking them to generate large amounts of signal and filter out the noise.

They include some detailed bug descriptions too, including a 20-year old XSLT bug and a 15-year-old bug in the <legend> element.

A lot of the attempts made by the harness were blocked by Firefox's existing defense-in-depth measures, which is reassuring.

Mozilla were fixing around 20-30 security bugs in Firefox per month through 2025. That jumped to 423 in April.
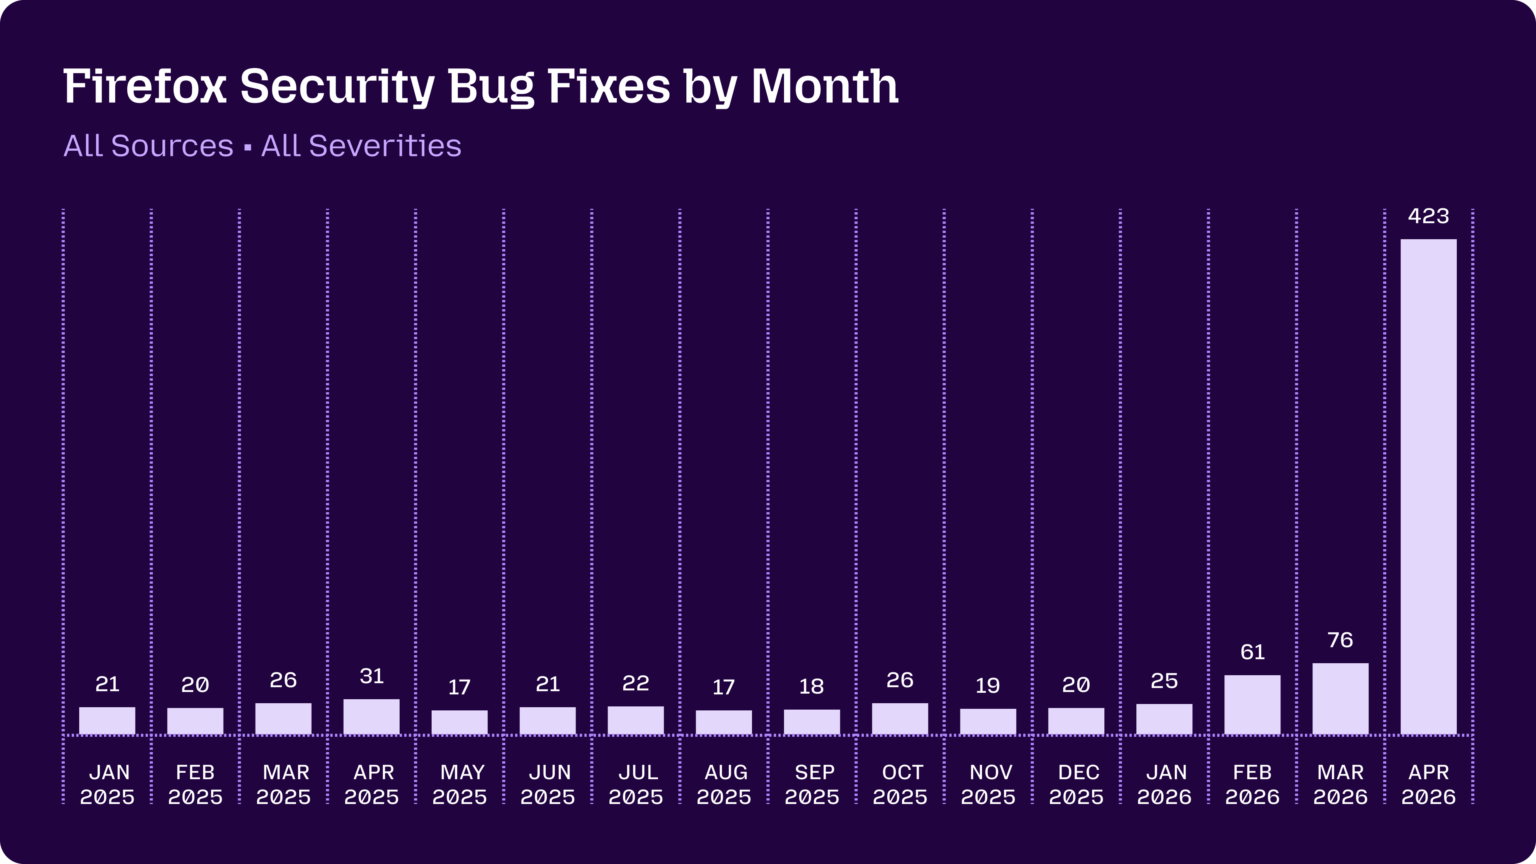
Bar chart titled "Firefox Security Bug Fixes by Month" with subtitle "All Sources • All Severities" on a dark purple background, showing monthly counts: Jan 2025: 21, Feb 2025: 20, Mar 2025: 26, Apr 2025: 31, May 2025: 17, Jun 2025: 21, Jul 2025: 22, Aug 2025: 17, Sep 2025: 18, Oct 2025: 26, Nov 2025: 19, Dec 2025: 20, Jan 2026: 25, Feb 2026: 61, Mar 2026: 76, Apr 2026: 423 — a dramatic spike in the final month.