





A staggering 40,003 total CVEs were recorded by the National Vulnerability Database (NVD) in 2024. Technology advancements and the rate at which features are continually released undoubtedly contribute to these rising numbers, which represent a 39% increase from 2023. Prioritizing security from the start by employing secure coding and development practices is key to mitigating vulnerabilities.
The cybersecurity risk landscape continues to evolve rapidly with the rise of threat actor sophistication and tooling. In 2024, attacks involving the exploitation of web application vulnerabilities increased significantly — by 180% — nearly triple that of the previous year.
What was once considered a controversial topic has gained widespread appeal as a crucial practice in the ongoing fight against threat actors and vulnerability exploitation. Ethical hackers and security researchers are revolutionizing today’s vulnerability management programs and reducing online risks by participating in Bug Bounty programs and disclosing vulnerabilities responsibly.
Okta supports and actively participates in responsible disclosure practices including a Bug Bounty program, which contributes to a safer online community by reducing the number of active vulnerabilities that could be exploited by threat actors with malicious intent. Industry benefits of responsible disclosures continue to grow for software vendors and technology users alike.
Traditional approaches to cybersecurity predate modern-day responsible disclosures and other notable programs such as BugCrowd or Project Zero. Organizations can now leverage the skillset of the hacker community to improve their security posture. Ethical hackers are provided an environment to learn, test, and responsibly disclose security issues to technology vendors.
The more testing, the better. Ethical hackers who attempt to discover software vulnerabilities with the intention of closing security gaps improve security posture. However, a Bug Bounty program should not replace a full-time security team; dedicated, internal talent, including Offensive Security or Product Security, is highly advisable. Ethical hacking programs should complement a comprehensively robust security program.
Bug Bounty programs offer organizations additional security safeguards while awarding monetary rewards to ethical hackers for successfully discovering and reporting bugs or vulnerabilities to the software vendor. The cost of an exploited vulnerability resulting in a data breach will far outweigh any Bug Bounty reward.
Trust starts with transparency: technology vendors are granted opportunities to be transparent with their customers, given the identification of vulnerabilities. Responsible disclosure programs aim to socialize ethical hacking practices further and improve vendor transparency by avoiding silent patching. Organizations are subject to NVD standards when remediating and communicating vulnerability-related information to customers and users.
Okta is proud to offer Bug Bounty programs through BugCrowd which create direct connections to the global security researcher community. Okta welcomes submissions and believes that community participation plays an integral role in protecting our clients’ systems and data.
On any given day, thousands of lines of code are written, and hundreds of thousands are released into production for the Okta and Auth0 platforms. These programs are a supplementary security practice to our standard Secure Development Lifecycle (SDL) methodologies which include in-depth reviews at various stages of development.
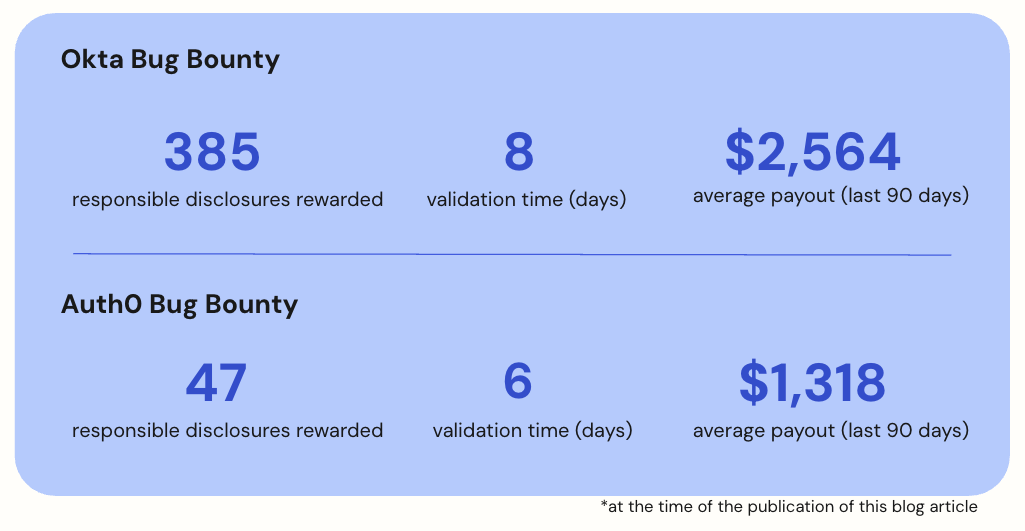
We invite you to review Okta’s defined Vulnerability Reporting Policy, which details the do’s and don’ts of security research for our Identity platforms and includes additional helpful guidance.
Watch Oktane 2024 On Demand to deep dive into Okta’s BugCrowd programs from our own Product Security experts. To learn more, including how to participate, read on about Okta’s BugCrowd and Auth0’s BugCrowd Bug Bounty programs.
Carmen Girardin is a Manager, Security Communications at Okta. Backed by over a decade of experience in the fintech sector, Carmen is a proficient technical writer with domain expertise in Identity and Access Management (IAM). She is passionate about delivering engaging, timely customer communications on the cybersecurity ecosystem and the evolving threat landscape, to help our customers gain the most value from Okta. Carmen spends her downtime traveling, thrifting for treasures and reading.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。