


 porn
Looking for a hentai game, but ended up with malware? Attackers are hiding the Argamal remote access Trojan inside hentai games, and distributing it through dedicated websites and torrent trackers. We break down how this malware works, why it’s dangerous, and how to keep your computer from becoming a goldmine for blackmailers.
In April 2026, we discovered a new campaign targeting users of hentai games. Attackers are embedding a remote access Trojan named Argamal into game installers. While concealing its presence, it can remotely control the computer and steal files and personal data.
Here’s how to avoid falling victim to this new Trojan — and how to safely and anonymously enjoy spicy content with (or without) anime girls.
How computers get infected with Argamal
Most of the infected games are distributed through adult game and torrent sites. In some cases, they are posted for download on file-sharing services and linked on gaming websites.
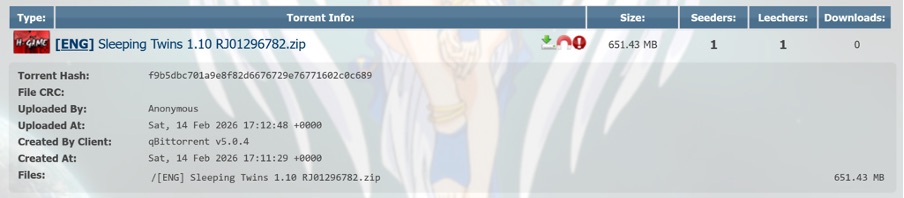
Example of a trojanized game hosted on the AniRena torrent tracker
Interestingly, instead of finding a dummy file inside the archive — as is often the case — the user gets the actual game built on popular engines like RenPy or RPG Maker. Infected pirated versions usually turn out to be scams: games fail to launch, folders are full of files with bizarre extensions, making it rather easy to put two and two together. Here, however, the user gets the actual gameplay they expected. Meanwhile, the Trojan lets itself in and keeps a completely low profile.
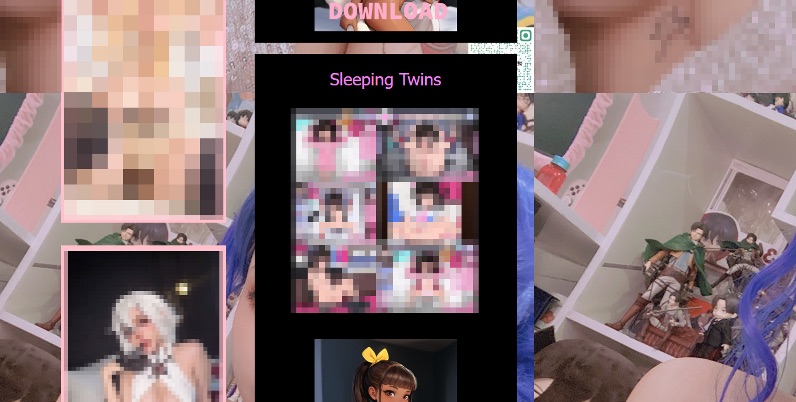
Example of a trojanized game hosted on the AniRena torrent tracker
Tucked right alongside the legitimate files in the archive is a DLL that the game relies on to run, but it’s been rigged: as soon as the user launches the game, the infected DLL automatically loads into memory. There are no outward signs of infection: neither an installer popping up in the background, nor a scary window or prompt asking you to disable your antivirus.
Argamal takes things real slow: instead of immediately rushing to steal files and passwords or throwing a digital rager on your computer, the Trojan first checks whether it’s running in a virtual machine or sandbox, and then goes into standby mode.
During this time, the malware writes hidden parameters to the system, conceals the paths to its DLLs, and delays its own execution. Three days later, the computer connects to GitHub, downloads an encrypted file, decrypts it, and turns it into a working Trojan module.
To ensure persistence, the attackers register the malware under the WindowsColorSystem Calibration Loader system task, a built-in Windows feature that triggers at every user logon to load monitor color profiles. Before shutting down, the malware deletes temporary files and covers its tracks to make it even harder to detect.
What makes Argamal dangerous?
Argamal is a remote access Trojan (RAT), which means attackers can use it to remotely control the victim’s computer. Here’s just a short list of what it may entail:
- Executing arbitrary commands on the computer
- Downloading and running files
- Checking if an antivirus is installed on the PC (by the way, our security solution detects and neutralizes Argamal before it can harm you)
- Searching for and exfiltrating sensitive data from files and system settings
- Taking screenshots and streaming video from the device
- Sending data to the attackers’ server
- Monitoring user activity
- Shutting down or restarting the device
Essentially, the infected computer turns into a remotely controlled machine. The owner may keep calmly going about their day, completely unaware that their device has been compromised. Yet the consequences of such an infection can be devastating.
For example, a single password stolen from a text note can lead to multiple compromised accounts at once if the victim reuses the same credentials across different sites. That’s why we recommend storing strong and unique passwords in an encrypted vault of a password manager rather than in plain text files.
Beyond hijacking accounts, the Trojan lets attackers literally spy on the user — reading their chats, digging into secret files, studying their sexual preferences… The cybercriminals can then use this highly sensitive information for subsequent attacks, blackmail, and extortion. We’ve covered what to do if you find yourself being targeted by extortionists in a previous post.
Another common scenario involves quietly stealing or substituting financial data — for instance, intercepting credentials from banking apps or replacing crypto-wallet addresses in the clipboard, which sends all your money straight to the attackers’ accounts.
In short, there’s a whole laundry list of ways attackers can exploit a victim’s device and data.
Argamal, yamete kudasai! How to protect yourself from similar threats
If you’ve decided to become the proud owner of “Waifu Simulator Ultra Definitive Edition”, stay on your guard:
- Use security software that runs in real time and catches sophisticated malware. Despite the attackers’ best efforts to make the Trojan invisible, Kaspersky Premium instantly detects and removes Argamal from users’ devices.
- Avoid downloading adult apps, installation files, and spicy content from untrusted sources. Clicking a “free XXX game, no signup needed” is a surefire way to invite malware onto your device. That said, even official platforms like Google Play and the App Store unfortunately let infected apps slip through the cracks at times. To stop worrying about accidentally downloading a Trojan or an infostealer, use Kaspersky Premium on all your devices.
- Don’t share more data than you absolutely have to. If an adult game or website insists you sign up, enter personal data, or link third-party accounts instead of just checking your birth date, that’s a huge red flag. Sites rarely collect sensitive data for no reason. In the best-case scenario, it ends up with marketers and ad trackers. In the worst-case, it falls into the hands of bad actors who will use it for blackmail, phishing, or breaking into your other accounts.
- Don’t click ad banners on adult websites. Even the most popular platforms like Pornhub occasionally host ads laced with malware. If you find it hard to hold back, use a security solution that will block malware downloads and prevent redirects to suspicious sites.