






By Ryan Tucker, Solutions Architect
Palo Alto Networks High Availability has been one of our most highly requested feature integrations with Megaport Virtual Edge. Now, it’s available. Here’s how you can use it for a more reliable, redundant network.
Architecting a network without operational resiliency would be like building a skyscraper without proper scaffolding. It might seem fine at first, but how will it survive over time or if there’s a severe weather event?
As multicloud, hybrid cloud, and cross-cloud setups become the norm and global workloads need to be in constant communication with each other, losing one connection can impact your entire network and compromise your bottom line. Having a network that’s always on has never been more important.
Having a resilient and highly available network does more than just protect against downtime and single points of failure – it allows you to customize your connectivity to suit each workload so you’re constantly getting the best possible performance.
If you’re already a Megaport customer, you know we take availability seriously. Many of our on-demand solutions are designed to improve and protect network availability across all of your cloud providers and global locations.
Megaport Virtual Edge (MVE) is a popular way for our customers to safeguard their network availability. With MVE you can deploy virtual instances like SD-WAN gateways, virtual routers, and virtual firewalls in minutes to improve performance and reliability.
Megaport Virtual Edge simplifies the deployment of diverse connections by establishing diversity zones. For maximum availability, customers may also deploy a pair of MVEs in different physical data centers, all within the same geographic metro region.
But for Palo Alto Networks customers, combining MVE with Palo Alto Networks VM-Series Next Generation Firewall (NGFW) unlocks a new level of availability.
Deploying VM-Series while leveraging its built-in High Availability (HA) functionality provides a robust solution that solves several firewall challenges, in particular session state and configuration synchronization, and orchestrated failover.
Palo Alto Networks VM-Series Firewalls deployed on MVE can now be configured with Active-Active HA, combining these benefits with Megaport’s on-demand as-a-service deployment, global reach, and direct private connectivity to clouds and data centers – the scaffolding needed for your skyscraper to last.
“Megaport offers hybrid and multicloud connectivity at scale, and simplifies diverse connections so they’re easy to manage. We’re thrilled to partner with Megaport, providing this new integration that gives Palo Alto Networks customers additional options for deploying our platform, ultimately increasing reliability and availability.”
– Pamela Cyr, Vice President Technical Partnerships, Palo Alto Networks
VM-Series has two HA modes: Active-Active and Active-Passive. As the name suggests with Active-Passive, only one firewall is active at any one time while the secondary firewall’s interfaces are all disabled and allow no traffic to pass. But for this post, we’ll be focusing on Active-Active which is supported by MVE.
Active-Active allows both firewalls to be active and allow traffic to pass at the same time. If a firewall or monitored link fails, all traffic is redirected to the remaining device. This setup has the advantage of making the rest of the network aware of available paths, and allowing the full capacity of both firewalls to be used in a normal state.
A failover can be triggered either by a firewall failure, a monitored path becoming unavailable, or a failure of the HA links between devices. If a monitored path becomes unavailable, traffic is forwarded from the affected device to the device with the available path.
Learn more about PAN-OS Active-Active HA in Palo Alto TechDocs.
We think a VM-Series virtual NGFW HA architecture underpinned by MVE is a perfect choice for a virtualized network core or better multi cloud connectivity, and our customers agree – our support team regularly answers requests to help deploy these network setups.
We’ve created a step-by-step guide in our Docs Portal that walks you through setting up your own VM-Series HA architecture on MVE. Be sure to bookmark the doc to return to whenever you need.
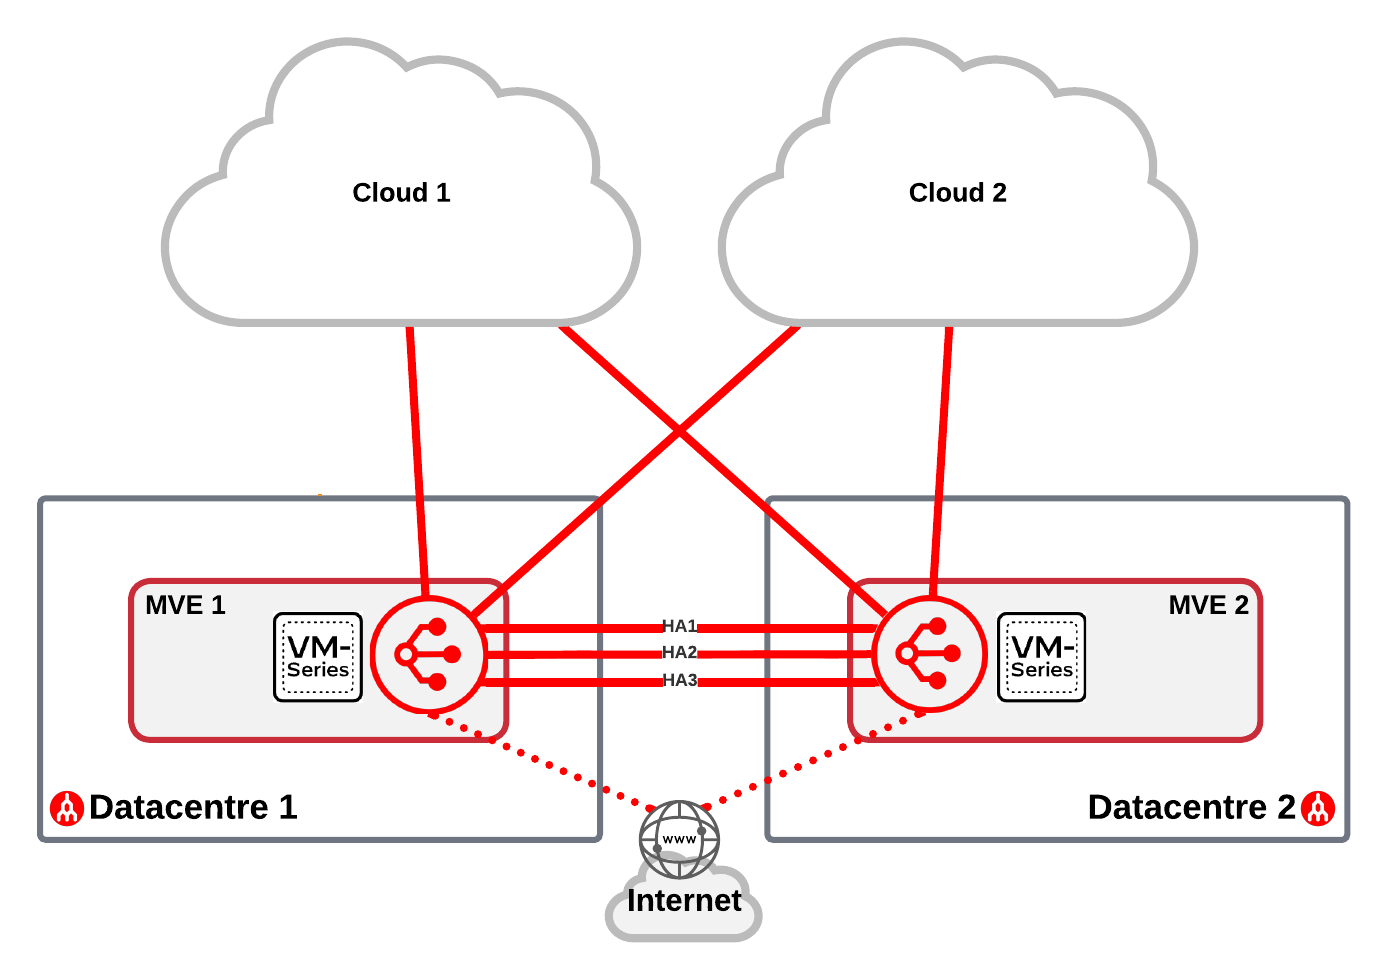
Configure High Availability on Palo Alto Networks VM-Series Virtual Firewall.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。