









AWS Outposts is a fully managed service that brings AWS infrastructure, AWS services, APIs, and tools to your data center, colocation space, or on-premises facility for a truly consistent hybrid experience.
1. What is AWS Outposts?
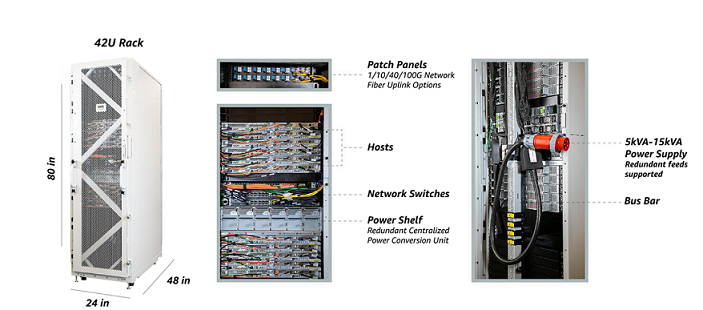
If you ask someone to describe an outpost, they might detail a historic outpost of the American frontier, like Fort Sedgewick in Dances with Wolves. AWS Outposts is a great name for the product. Launched at the re:Invent 2018, AWS Outposts is a single rack, exact replica of what AWS runs in their own data centers and delivers a fully managed, consistent hybrid cloud experience. AWS will actually visit your data center or colocation facility, install the Outposts hardware and configure it to connect back to the nearest AWS Region. Once configured, the Outposts is managed, monitored, and updated by AWS just like in the cloud.
2. Why would an organization need Outposts?
Customers can use Outposts to run AWS services like EC2, EBS or RDS locally (and since September 2020, S3 is now available too). This can address workloads with certain requirements around local data residency or ultra-low latency processing.
Another business driver is disaster recovery, especially in countries where there is only one AWS Region. In Canada, for example, the government mandates that a recovery setup is a “safe distance” from the primary site, but for data sovereignty, the setup must remain in-country. Outposts can be used to effectively create a substitute second region to ensure compliance.
But the greatest advantage lies in how Outposts simplifies hybrid IT operations. Without Outposts, one team would typically manage the on-premises infrastructure (patches, security, and networking) while another team would own the public cloud environment and associated operations. In a hybrid Outposts-based infrastructure, a single AWS Console can be used to manage the same services running in the cloud and locally–massively streamlining IT operations.
Learn more about data sovereignty in Canada and how Megaport Cloud Router can help.
3. AWS Outposts connectivity
Connectivity is critical to Outposts–firstly, to your on-prem (LAN) and secondly, back to the parent AWS Region (WAN)–so let’s look at both in more detail.
Physical: From a physical perspective, customers will connect the Outposts switches “north” to their on-premises network (router/switch/firewall) via a pair of single or multi-mode fibres with speed options of 1/10/40/100 Gbps.
Logical: Across these Ethernet links, AWS requires two different VLANs to logically separate and route the Outposts traffic either back to the AWS Region (via a service link VPN to public AWS endpoints) or to your LAN (known as LGW or Local Gateway). Both the LGW and service link VLANs will each need at least a private /26 subnet assigned by the customer.
Local Area Network (LAN): From a local network perspective, Outposts has the same entities as a normal VPC (subnets, route tables, and ACLs) but to enable communication to your local area network, AWS introduced the LGW. The LGW’s primary role is to connect into the on-prem LAN, but it also enables connectivity to the internet. The LGW functions in a similar way to an Internet Gateway (IGW), so in the Outposts route table, there will be entry sending all on-prem IP traffic to the LGW. The LGW will learn and exchange routes with your premises networking via BGP.
Wide Area Network (WAN): In terms of connectivity back to the parent AWS Region,things get more interesting. AWS recommends the use of dual 1Gbps connections back to the parent region. Pulling a new Amazon Machine Image (AMI) for a new EC2 could be painfully slow with anything less.
The first option is over a standard internet connection. When Outposts turns on initially, it will call back to the parent region and connect to the AWS Outposts service anchor (via Amazon public IPs) and build an encrypted set of VPNs known as a service link. This service link is how AWS manages the on-prem Outposts infrastructure and inter-VPC/Outposts traffic. The customer’s firewall must be opened up for outbound connections back to the parent AWS Region (and inbound, if not stateful).
The second option is to use a Direct Connect with a public VIF, either dedicated from AWS or a partner such as Megaport. This will provide higher speed, lower latency for the traffic between your VPC and on-prem Outposts with much lower Data Transfer Out (DTO) fees. However, it still uses AWS public prefixes which means the public VIF will advertise all of the Amazon public ranges to your local router (almost 5,000 prefixes).
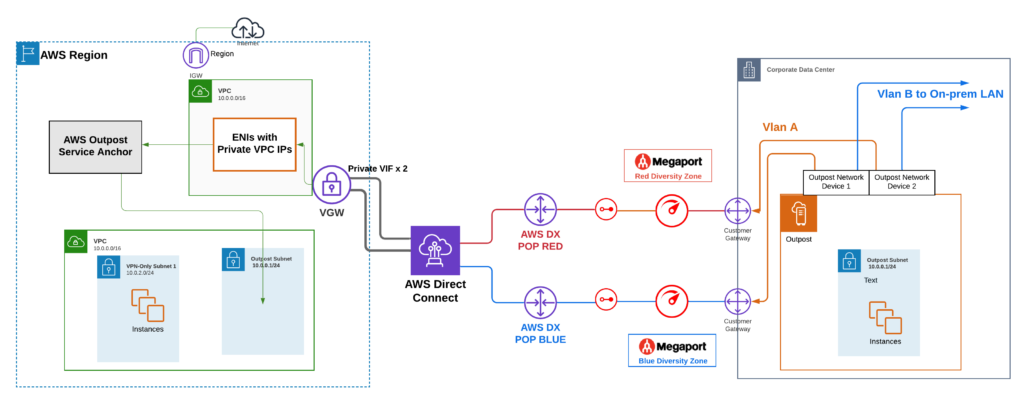
In December 2020, AWS announced the launch of Outposts private connectivity. A welcome alternative to the public internet or public VIF options. This means the endpoint for the service link can now be a set of private elastic network interfaces (ENIs) situated within an AWS VPC through a VGW using a private VIF. Outposts traffic no longer has to travel across the public internet, and you don’t have to manage large public IP allow-lists on your local firewall. Connectivity to Transit Gateway is currently not supported for Outposts.
Example using Megaport and Hosted Connections/Private VIF
The diagram below shows an AWS Outposts deployment in a colocation facility using Megaport to connect back to the parent VPC. This is a highly available design, as it utilizes dual 10G Megaport Ports split across the recently launched diverse blue/red zones (select metros only), and similarly also uses two hosted connection links provisioned on diverse red/blue AWS routers at the AWS on-ramp. Both VXCs are connected to the Direct Connect Gateway and then attached to the parent VPC via private VIFs.
Conclusion
As enterprises continue moving to a hybrid infrastructure, the challenge will be to avoid operational complexity. AWS is clearly going all in on hybrid cloud, releasing a number of product updates to Outposts last year. Firstly they launched support for S3 and EC, and at re:Invent 2020, they also released smaller Outposts form factors (1U/2U rack mountable servers) targeting “branch offices, factories, retail stores, health clinics, hospitals, and cell sites that are space-constrained and need access to low-latency compute capacity.”
Outposts allows IT teams to reuse their experience with AWS and apply it to local on-prem environments. Megaport can help simplify Outposts connectivity by delivering high-speed, private links to AWS utilizing the original public VIF or the newer private VIF options. Using red/blue diversity zones on both Megaport and AWS, Outposts customers can enjoy high availability at both the edge and on-ramp tiers.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。