



惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

J
Java Code Geeks
Stack Overflow Blog
Stack Overflow Blog
P
Proofpoint News Feed
L
LangChain Blog
C
Check Point Blog
F
Fortinet All Blogs
Cyber Security Advisories - MS-ISAC
Blog — PlanetScale
Blog — PlanetScale
腾讯CDC
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
Jina AI
Jina AI
Recent Announcements
雷峰网
雷峰网
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
N
Netflix TechBlog - Medium
博客园 - 【当耐特】
Hugging Face - Blog
Hugging Face - Blog
Microsoft Azure Blog
U
Unit 42
The Cloudflare Blog
月光博客
月光博客
有赞技术团队
有赞技术团队
G
Google Developers Blog
Vercel News
Vercel News

Megaport Blog

A Guide to NAT Gateway A Guide to Cloud Storage How the Data Center Is Evolving in 2026 What to Expect When Attending Your First Network Operator Group (NOG) Nine Ways to Connect to Cloud Using Private Connectivity Migrate Your On-premises to the Cloud: A Step-by-Step Guide How to Lower Your Egress Fees in 2026 How to Achieve Data Sovereignty in Europe Cisco and Megaport: Redefining the Edge of Modern Networking How to Reduce Latency in Your Multicloud Environment Introducing Megaport High-Speed Cross-Cloud Encryption Are Businesses Leaving the Cloud? Using Meraki and Megaport Virtual Edge for Multicloud Networking Equinix Metal® is Going Away: Here’s What You Can Do Introducing Megaport On-ramp as a Service Megaport’s Full Solution Portfolio Is Coming to India New Bare-metal GPU Instance Now Available with NVIDIA RTX Pro 6000 A Look Back at 2025: Megaport's Biggest Updates Megaport Expands Into India With Strategic Acquisition of Extreme IX Your 2026 Predictions From AWS re:Invent 2025 What’s Next for NaaS? Top Trends for 2026 What is IPsec? When to Move From Public Internet to Private Connectivity Megaport and Latitude.sh: Bringing Compute and Connectivity Together How to Improve Your Microsoft ExpressRoute Resilience with Megaport Connectivity Comparing Ways to Connect to AWS What is API-First Networking? The Hidden Cost of Running Cloud-Hosted SD-WAN for IaaS How to Overcome NaaS Integration Challenges Introducing SCION with Anapaya and Megaport
Portal Highlight: Service Groups
Megaport · 2014-07-24 · via Megaport Blog

A common complaint we hear about regarding supplier web portals is that if a single person needs access to multiple companies, that person generally needs to maintain multiple accounts.

One of the core concepts in the Megaportal is the idea that all our services belong to a Service Group. A Service Group is owned by a company and permissions are granted against the Service Group. Services can belong to multiple service groups, and people or roles can be assigned access to multiple service groups. Permissions can be granted to people or roles, we’ll get to this in a moment.

Users & Roles

Users are employed by one or more companies and all users have a Role or Position assigned to them. This might be a job title, department or term that is significant to you and your company. Users can be granted permissions directly on a Service Group. You can take a more powerful approach though and assign a Role permissions on a Service Group. This way you can give your NOC team permission to view and modify services, and any new NOC staff that are added later automatically inherit the permission.

Service Agents

Implementing Service Agents is another concept that we feel is important in the Megaportal. Service Agents are users that can be “invited” to another company. For example, a customer can invite a third party contractor and grant the contractor select permissions to act on their behalf.
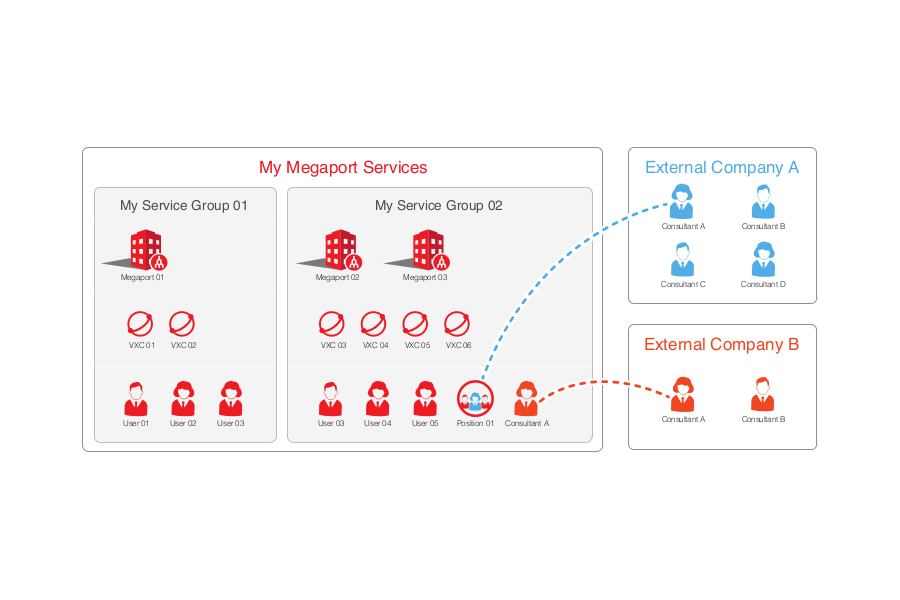
Take this example:

Service inheritance

This company has separated their services under two Service Groups and added users to the groups they need access to. They also outsource some work to external companies who also need limited access to some of the services. The example above illustrates how these links work. A consultant from External Company A is assigned a position from the company which grants them any permissions inherited from that role. A consultant from External Company B has been added to Service Group 2 individually so the permissions applied to that user can be fine-tuned. It’s a simple example but the system is designed in such a way that it allows complex configurations.

Conclusion

We’re always looking for ways to improve and simplify the customer experience. If you have any ideas on things we can do to make the portal or the phone apps better, please make sure to let us know.