








Endpoint attacks rarely appear in a single alert. Instead, they surface as a sequence of signals that require rapid investigation and response. For many teams, the challenge is not detection. It is having the time and expertise to investigate, validate, and then act.
Arctic Wolf Aurora Managed Endpoint Defense addresses this by combining endpoint detection and response with expert Arctic Wolf analysts who take on the operational burden. The result is faster investigations, guided response, and stronger endpoint defense without adding internal workload.
In many attack scenarios, multiple alerts can trigger within minutes. These may include a suspicious file flagged as ransomware, unauthorized script execution, credential access attempts, or disabled security controls.
Instead of pushing this workload to our customers’ internal teams, Arctic Wolf analysts immediately step in. They review, correlate, and validate alerts, grouping related activity into a single incident. This allows customers to avoid manual alert triage, gain rapid context across related activity, and see prioritized incidents instead of disconnected signals. Customers maintain full visibility through a shared incident view, but the investigation work is handled by Arctic Wolf, which removes the need for teams to interpret alerts under pressure and accelerates time to response.
Once an incident is identified, Arctic Wolf analysts drive the investigation end to end. Built-in AI supports this process by surfacing key insights, such as suspicious scripts or attacker behavior. Analysts then take direct action to validate and expand the investigation. This includes:
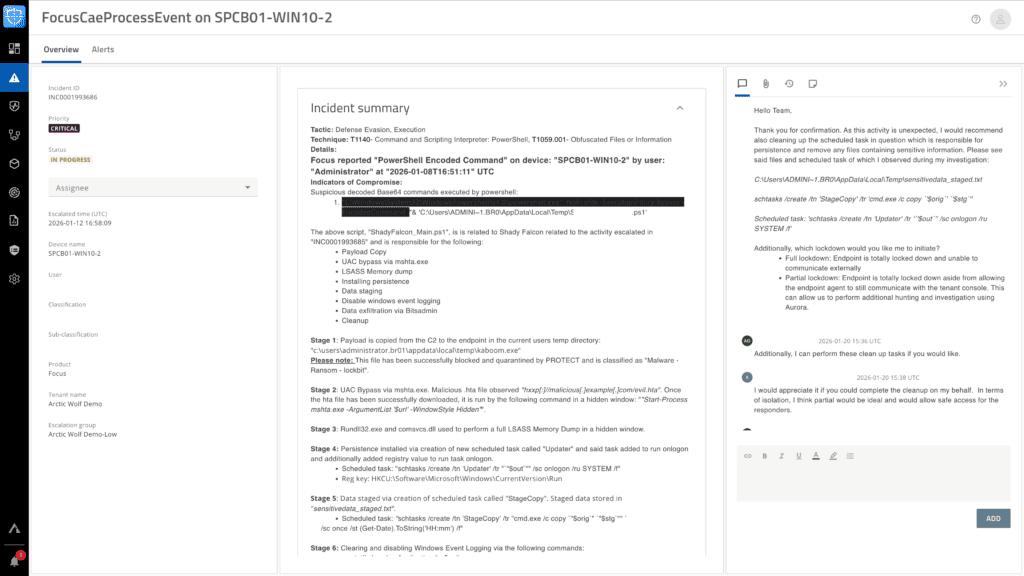
Screenshot of an Incident in Aurora Managed Endpoint
By combining AI-driven insight with hands-on analyst expertise, investigations move faster and with greater accuracy. Customers are not required to perform forensic analysis or manage investigation workflows.
Many organizations struggle with the transition from detection to action. Alerts are identified, but response is delayed due to limited resources or limited visibility. Aurora Managed Endpoint Defense eliminates this gap by enabling Arctic Wolf analysts to drive response while keeping customers fully informed.
Within each incident, analysts:
While Arctic Wolf handles investigation and response, customers remain informed and aligned through a shared experience, enabling them to review progress in real time without needing to coordinate or execute every step themselves.
Arctic Wolf has designed our managed experience so that organizations can easily review investigation summaries and validate whether activity is expected or suspicious. As customers review the investigation context, they can communicate directly with analysts to eliminate any potential concerns or work through anomalous activity.
Plus, with each investigation, Arctic Wolf provides clear remediation steps that will be taken, and customers can track remediation progress in real time. This model ensures alignment with business context while removing operational strain on internal teams.
Managing endpoint security internally requires continuous tuning, investigation, and response. These activities are critical but difficult to scale. Aurora Managed Endpoint Defense reduces this complexity by taking ownership of monitoring and alert triage, threat investigation and validation, response and containment actions, and ongoing tuning and optimization. This results in faster response times and improved protection without increasing internal effort.
Effective endpoint security depends on more than technology. It requires the right expertise, workflows, and execution, allowing organizations to achieve stronger protection and faster outcomes without the operational burden of managing endpoint security on their own.
Watch the full demo to see how Arctic Wolf analysts detect, investigate, and respond to endpoint threats:
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。